 Built by
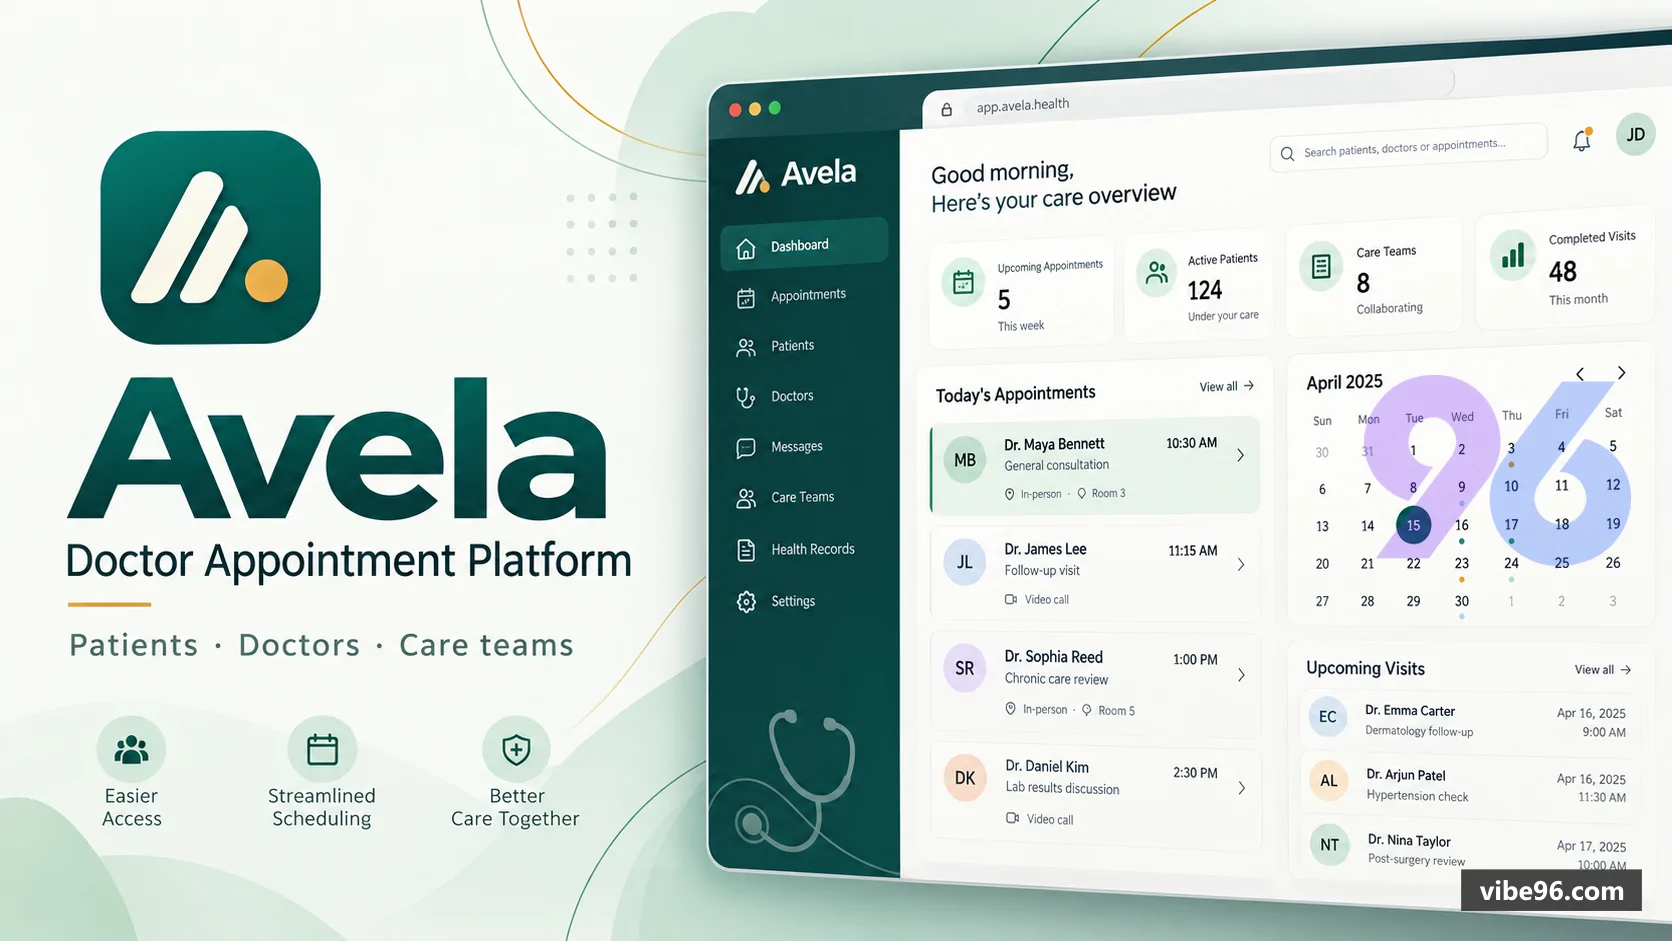
Why Avela - Clinic Management Software
What makes it better
than the alternatives
- 01
Three-role architecture
Separate patient, doctor and administrator interfaces with scoped data access and role-specific bootstraps
- 02
Session-based booking with capacity control
InnoDB row locks prevent overbooking; foreign keys cascade appointment deletions automatically
- 03
International phone validation
Integrates intl-tel-input library with 40+ language translations and libphonenumber-for-php backend validation
- 04
Docker Compose deployment
Single-command setup with MariaDB health checks, environment-based configuration and automated schema initialization
- 05
Hardened authentication flow
Password hashing with password_hash/verify, CSRF tokens on all mutations, and session regeneration on login
Authentication & Registration
- Public login page with email/password authentication
- Patient self-registration with phone number validation
- Password hashing using PHP password_hash (bcrypt)
- CSRF token validation on all POST requests
- Session regeneration and secure cookie flags
Patient Portal
- Dashboard showing upcoming appointments and statistics
- Doctor directory with search and specialty filtering
- Session browsing and appointment booking
- Appointment cancellation with confirmation dialogs
- Profile settings with password change and account deletion
Doctor Portal
- Dashboard with appointment counts and patient lists
- Session creation and management (date
- time
- capacity)
- Appointment viewing filtered by doctor's own sessions
- Session cancellation with cascade deletion of bookings
- Profile editing and password management
Administrator Portal
- Full clinic dashboard with system-wide statistics
- Doctor account creation
- editing and removal
- Patient directory with search and filtering
- Session management across all doctors
- Appointment oversight and cancellation capabilities
Session & Booking Engine
- Session scheduling with date
- time and patient capacity
- InnoDB FOR UPDATE row locks during booking to prevent races
- Capacity validation before confirming appointments
- Foreign key constraints cascade session deletions to bookings
- Transaction-wrapped multi-table updates for consistency
Database Layer
- MariaDB 11.4 with InnoDB storage engine
- Prepared statements for all user-supplied SQL values
- Foreign keys between webuser
- doctor
- schedule and appointment tables
- Health check queries in Docker Compose startup
- Schema and seed SQL files for fresh installations
Deployment & Configuration
- Docker Compose with web and db services
- Environment variable configuration for database and passwords
- Automated schema initialization on first container start
- CLI initialize.php script sets admin and demo passwords
- Apache with mod_rewrite for extensionless URLs
Security & Testing
- Python authorization test suite verifies role boundaries
- Smoke tests for public routes and signed-out restrictions
- CSRF rejection tests for all mutation endpoints
- Role guard checks precede all code in protected routes
- No passwords in seed SQL or browser hints
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| JavaScript | — | — | Front-end | 77.5% |
| PHP | — | — | Web, API | 10.1% |
| CSS | — | — | Styling | 7.5% |
| TypeScript | — | — | Front-end | 3.8% |
| SQL | — | — | Database | 0.9% |
| Python | — | — | Web, API | 0.3% |
| HTML | — | — | Front-end | 0% |
- Primary language
- PHP 8.4
- Framework
- None (vanilla PHP)
- Database
- MariaDB 11.4
- Authentication
- Session-based with password_hash/verify
- Licence
- Single-site
- Screens
- 28
- Database tables
- 7
- Supported languages
- English
- Browser support
- Modern browsers (Chrome, Firefox, Safari, Edge)
| Minimum | Recommended | |
|---|---|---|
| CPU | 1 vCPU | 2 vCPU |
| RAM | 1 GB | 2 GB |
| OS | Debian/Ubuntu with Apache 2.4, PHP 8.4, MariaDB 11.4 | Debian/Ubuntu with Apache 2.4, PHP 8.4, MariaDB 11.4 |
| Est. monthly hosting | $10 | $10 |
```bash
cp .env.example .env
# Edit .env: set DB_PASSWORD, DB_ROOT_PASSWORD, INIT_ADMIN_PASSWORD
docker compose up -d
# Access at http://localhost
# Login: admin@example.com with INIT_ADMIN_PASSWORD
```
```bash
sudo apt update && sudo apt install -y apache2 mariadb-server php8.3 php8.3-mysqli php8.3-mbstring composer nodejs npm
sudo mysql -e "CREATE DATABASE edoc; CREATE USER 'avela'@'localhost' IDENTIFIED BY 'YOUR_PASSWORD'; GRANT ALL ON edoc.* TO 'avela'@'localhost'; FLUSH PRIVILEGES;"
cd /var/www/html
sudo git clone https://github.com/your-repo/avela.git .
sudo composer install --no-dev
sudo npm ci --omit=dev && npm run vendor:phone
sudo mysql edoc < database/schema.sql
sudo mysql edoc < database/seed.sql
cp .env.example .env
# Edit .env with database credentials and INIT_ADMIN_PASSWORD
sudo php scripts/initialize.php
sudo chown -R www-data:www-data /var/www/html
sudo a2enmod rewrite
sudo systemctl restart apache2
```
```bash
# In Coolify dashboard:
# 1. Create new service from Docker Compose
# 2. Paste docker-compose.yml content
# 3. Set environment variables:
#    DB_PASSWORD, DB_ROOT_PASSWORD, INIT_ADMIN_PASSWORD
# 4. Deploy
# Service will auto-initialize on first run
```
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
92/ 100
Automated audit score
✓ Passed the auditReviewer notes (3 minor)
Database access is parameterized; schema lacks indexes on several foreign keys; dependencies mostly current; minor outdated packages but no critical vulnerabilities; moderate duplication across role-specific pages; some oversized files and hard-coded values. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.