 Built by
About this software
About Kinroll - Membership Management System
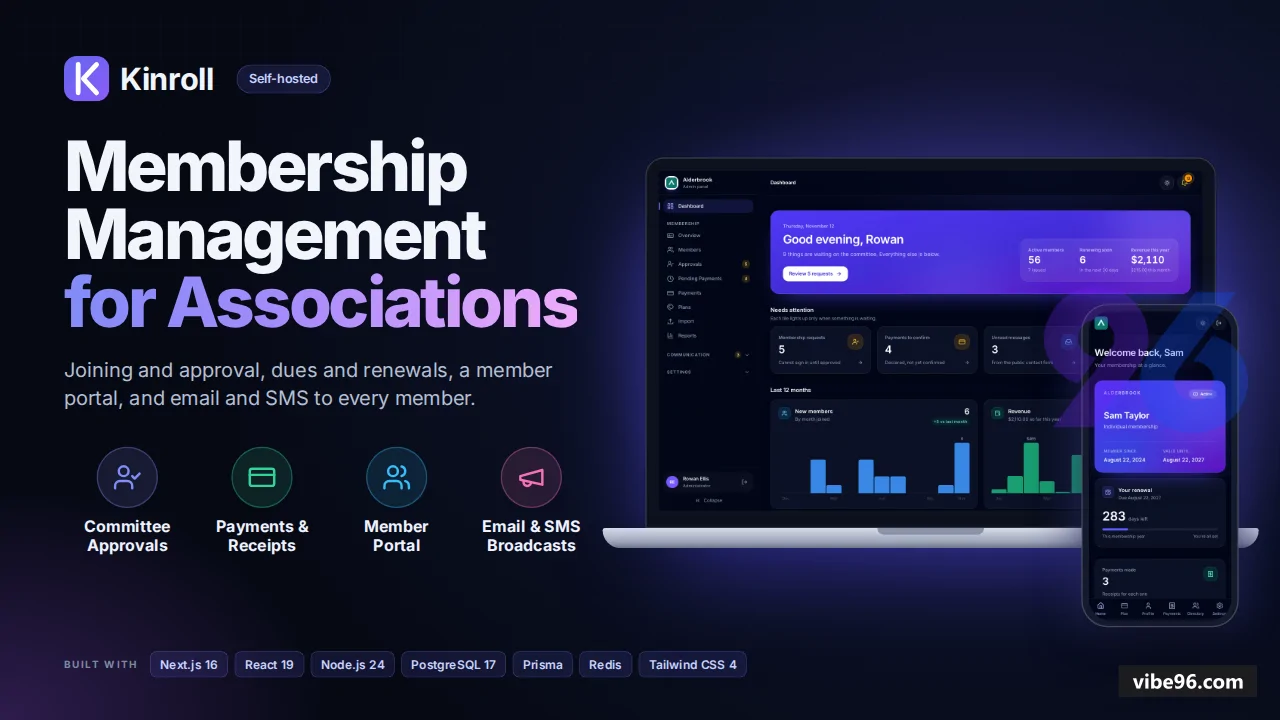
Kinroll is a membership management system for one association per installation, built as a Node.js/Express API, a separate background worker (BullMQ on Redis) and a Next.js 16/React 19 web app on PostgreSQL via Prisma. It covers public joining with email verification and committee approval, yearly and lifetime plans, Stripe card payments and staff-confirmed offline payments, plus a member portal with an opt-in directory. Staff can send email broadcasts through their own SMTP accounts and SMS through configurable HTTP gateways, with queues, retries and unsubscribe handling. The admin panel has permission-based staff types, an activity log, reports and CSV/Excel member import. The web app has roughly 90 page routes: 12 public/member-facing pages, 6 portal pages and about 55 admin screens. There is no mobile app. Docker, PM2/Nginx and Render deployment guides are included.
Why Kinroll - Membership Management System
What makes it better
than the alternatives
- 01
Approval-first joining
New members register, verify their email and wait in a committee approval queue; approval is re-checked on every portal request so revocations take effect immediately.
- 02
Stripe plus offline payments
Card checkout and refunds through Stripe, alongside offline payment methods that staff confirm, with webhook handling in the backend.
- 03
Built-in email and SMS broadcasting
Own SMTP accounts, templates, scheduling, delivery queues, suppression lists and a separate worker process, with SMS via any HTTP gateway configured in the admin panel.
- 04
Granular staff permissions
Staff user types carry per-area permissions, with a protected administrator account, login lockout, idle-timeout sessions and an activity log.
- 05
Heavily tested and documented
Backend integration tests (including authorization tests across every route), Vitest frontend tests, Playwright e2e with accessibility checks, and 35 markdown docs including admin and member manuals.
Joining & Approvals
- Public join wizard with email verification
- Committee approval queue with notes on refusal
- Optional Sign in with Google
- Optional reCAPTCHA bot protection
- IP rate limits on public forms
Plans & Payments
- Yearly and lifetime plans
- Stripe Checkout with webhooks
- Offline payment methods confirmed by staff
- Pending payments view and payment history
- Currency set in organisation settings
Member Records & Import
- Member list with search and filters
- CSV and Excel import with default-password flow forcing a password change
- CSV export
- Reports on growth
- revenue
- plans and renewals
Member Portal
- Membership status and renewal
- Payment history
- Profile and notification preferences
- Opt-in member directory
- Self-service account deletion request
Email Broadcasting
- SMTP accounts and domains
- Templates
- recipient groups and scheduled campaigns
- Delivery queue with retries and health monitoring
- Suppressions and one-click unsubscribe
SMS Broadcasting
- Configurable SMS providers and sender identities
- Lists
- templates and campaigns
- Delivery reports and inbound webhooks
- Opt-out suppression and queue management
Reminders & Notifications
- Renewal reminders via worker
- Editable notification templates
- Admin notification bell and contact-form inbox
Administration & Security
- Staff users and permission-based user types
- Activity log with retention settings
- Branding and organisation settings
- Login lockout and session policy
- Command-line user management tool
Operations
- Docker Compose and Render blueprint
- PM2/Nginx deployment guide
- GitHub Actions CI
- Backup/restore check script
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| JavaScript | — | — | Front-end | 55.5% |
| JavaScript (React) | — | — | Front-end | 36.6% |
| SQL | — | — | Database | 7.5% |
| CSS | — | — | Styling | 0.4% |
- Primary language
- JavaScript (Node.js 24) with JSX, CommonJS backend
- Framework
- Express 4 (API) and Next.js 16 with React 19 (web)
- Database
- PostgreSQL 17 via Prisma 5, with Redis for job queues
- Authentication
- JWT access and refresh tokens, bcrypt passwords, optional Google Sign-In and reCAPTCHA
- Licence
- Single-site
- Screens
- 66
- Database tables
- 35
- Supported languages
- English interface; no translation files in the digest. No RTL support
- Browser support
- Current Chromium, Firefox and WebKit (Playwright end-to-end tests)
| Minimum | Recommended | |
|---|---|---|
| CPU | 2 vCPU | 4 vCPU |
| RAM | 4 GB | 8 GB |
| OS | Linux with Node.js 24, PostgreSQL 17, Redis; Docker or PM2 + Nginx | Linux with Node.js 24, PostgreSQL 17, Redis; Docker or PM2 + Nginx |
| Est. monthly hosting | $40 | $40 |
```bash
cp backend/.env.example backend/.env
# edit backend/.env: JWT_ACCESS_SECRET, JWT_REFRESH_SECRET, UNSUBSCRIBE_SECRET, ENCRYPTION_KEY, DEFAULT_ADMIN_PASSWORD
POSTGRES_PASSWORD=YOUR-DB-PASSWORD docker compose up -d --build
```
```bash
npm run install:all
npm --prefix backend run prisma:generate
npx --prefix backend prisma migrate deploy
npm --prefix frontend run build
pm2 start backend/ecosystem.config.js
```
Use the included `render.yaml` Blueprint.
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (4 minor)
No real credentials found; demo password is published and .env.example uses weak jwt placeholders; prisma orm used with parameterised queries; schema files not fully reviewable, so score is capped; auth primitives look sound, but most routes and ownership checks could not be traced; mostly reproducible; one script target is missing and several setup gaps remain. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.