About this software
About SwiftCart
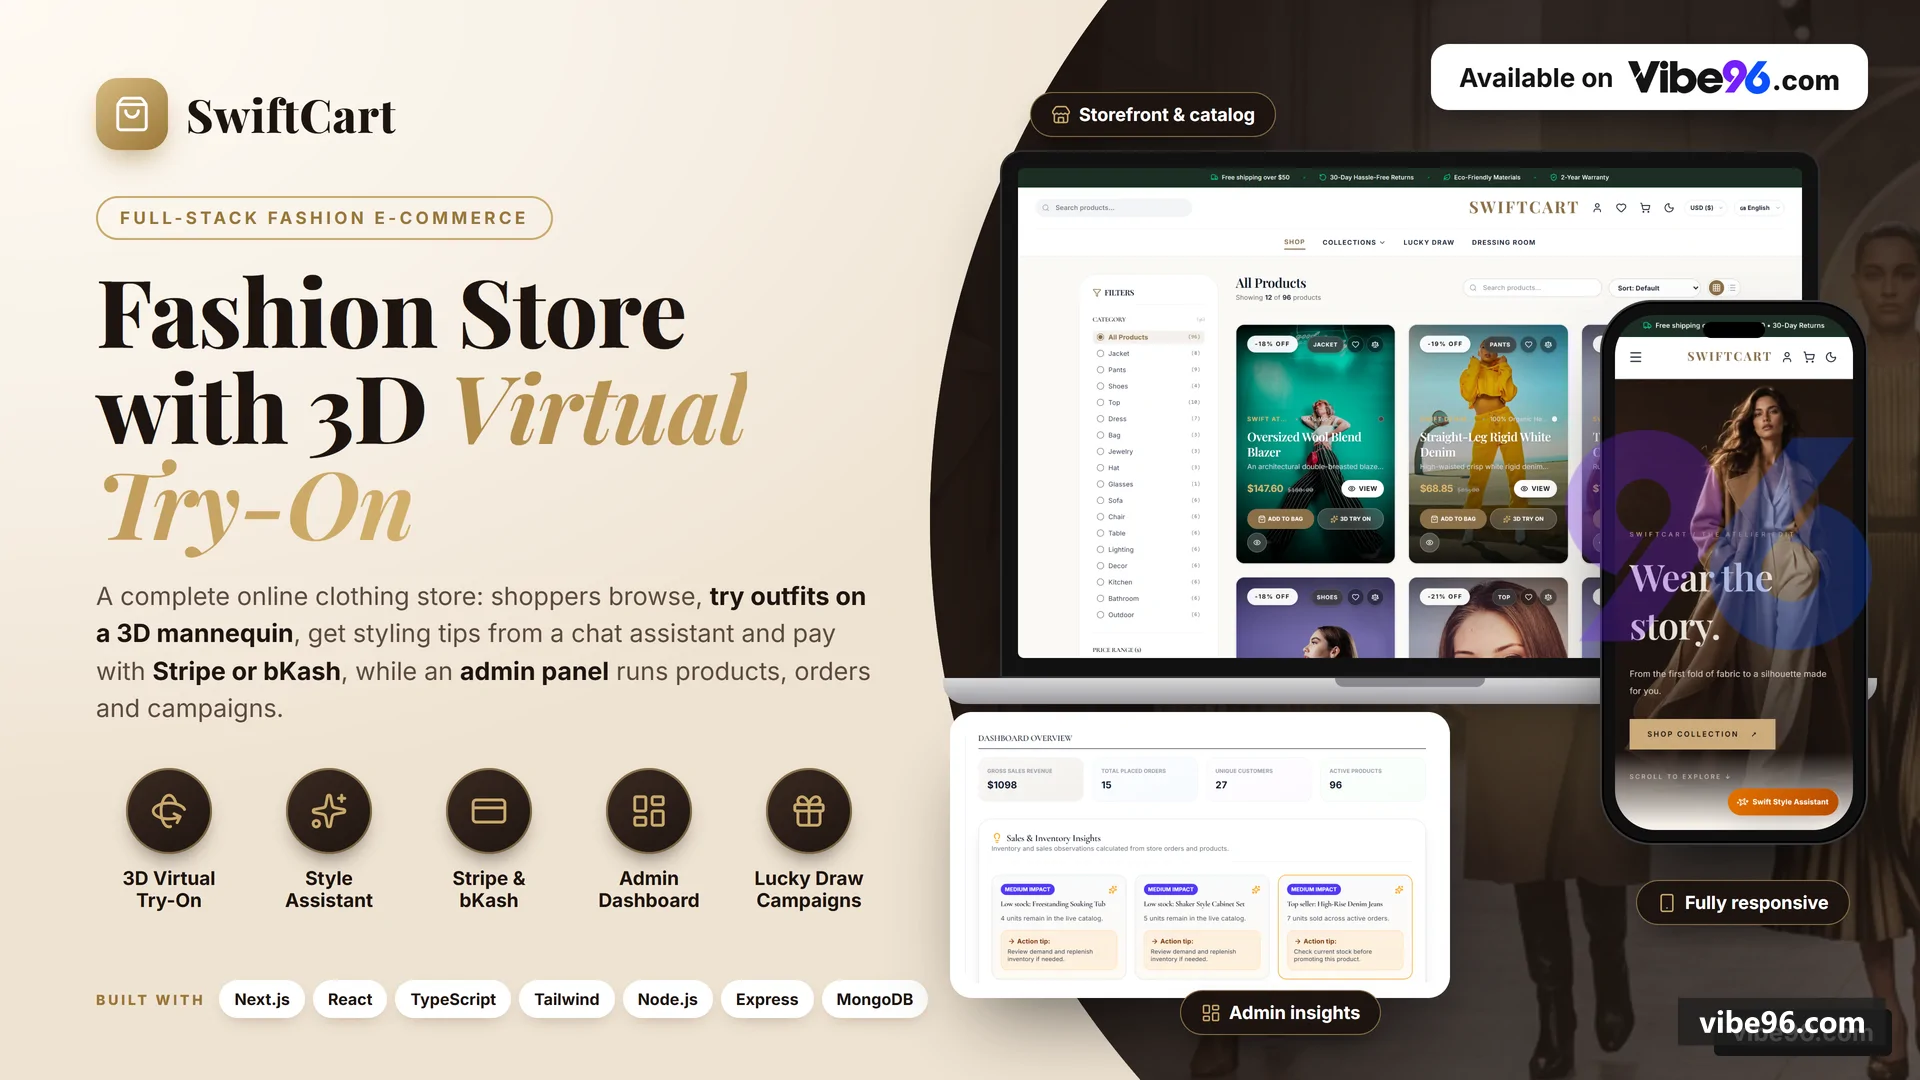
SwiftCart is a fashion shop built with a Next.js 16 / React 19 frontend and an Express + Mongoose backend, with 28 MongoDB collections. The storefront covers products, cart, checkout, wishlists (including shared links), orders, returns, reviews and lucky-draw campaigns, with a 3D dressing room built on Three.js. An admin panel at /admin manages orders, users, coupons, categories, currencies, languages, reviews, newsletter, wallet and reports. Payments are wired for Stripe (card) and bKash, with COD always available. Sign-in options include password, email code, Google Sign-In and TOTP two-factor, backed by rate limiting, token-versioned JWT sessions and a backend test suite. Some AI features are visible only as frontend component names in the digest, so their backend depth was not verified.
Why SwiftCart
What makes it better
than the alternatives
- 01
Layered sign-in security
Password, emailed OTP, Google Sign-In with nonce checks, and TOTP 2FA with recovery codes, plus login lockout and rate limiting.
- 02
D virtual dressing room
Three.js components (FittingRoom3D, DressRoomViewer, try-on body and garment modules) with a dedicated /dressing-room page.
- 03
Two payment gateways plus COD
Stripe card checkout and bKash tokenized checkout with a USD to BDT conversion, and a dev-only mock gateway; unpaid orders auto-expire.
- 04
Broad admin panel
Admin sections for orders, returns and refunds, coupons, currencies, languages, wallet, monitoring, activity logs, audit trail and reports.
- 05
Documented and tested
Swagger API docs, BRD and SRS files, setup guides, seed scripts with safety guards, and Node and Playwright tests.
Storefront
- Product listing
- product detail and shop pages with search service
- Image gallery
- variant selector and mobile sticky cart
- Product comparison modal and sticky compare bar
- Back-in-stock alert form
- Reviews section
Cart, Checkout and Orders
- Cart and checkout pages with server-side order quote
- Order history and order lifecycle service
- Return request modal and refund status/offer cards
- Coupon service
- Inventory handling
Wishlist and Campaigns
- Wishlist with shareable token page
- Campaign pages and my-tickets page
- Lucky-draw logic covered by draw-flow tests
Accounts and Security
- Register
- login
- forgot/reset password
- Email OTP login and Google Sign-In (link to existing account)
- TOTP two-factor with recovery codes
- Address book
- profile and settings pages
- Demo login buttons (disabled by default)
Payments
- Stripe card checkout with optional webhook
- bKash tokenized checkout
- Cash on delivery
- Store wallet with statements and manual adjustments for super admins
Admin Panel
- Dashboard overview
- reports and insights
- Orders
- users and role management
- user cart and wishlist views
- Coupons
- categories
- currencies
- languages administration
- Reviews
- contact messages
- chat messages
- newsletter
- Customer email modal
- activity logs
- audit trail
- monitoring
- Product dashboard with create
- edit and view pages
AI and Styling
- Floating AI stylist chatbot component
- Outfit builder
- AI picks and smart search components
- Product description and image enhancer components
- review analyzer
- Avatar profile and try-on modal
- Admin copy-draft endpoint that builds product text from templates
Platform and Tooling
- Cloudinary image uploads with Multer and Sharp
- SMTP email via Nodemailer
- Swagger UI at /api-docs
- Seed
- db:init and schema export scripts
- Backend tests and Playwright browser test
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| TypeScript (React) | — | — | Front-end | 58.9% |
| JavaScript | — | — | Front-end | 30.7% |
| TypeScript | — | — | Front-end | 9.2% |
| CSS | — | — | Styling | 0.9% |
| SQL | — | — | Database | 0.2% |
- Primary language
- JavaScript (Node.js 20.9+) with TypeScript 5.9 on the frontend
- Framework
- Next.js 16.4.2 (App Router, React 19) frontend with Express 4.22 backend
- Database
- MongoDB with Mongoose 8 (Atlas in production); minimum server version not stated in the digest
- Authentication
- JWT access tokens with HttpOnly refresh-token cookie, bcrypt password hashing, email one-time-code sign-in, TOTP two-factor authentication with recovery codes, and Google Identity Services sign-in
- Licence
- Single-site
- Screens
- 31
- Database tables
- 28
- Supported languages
- Admin-managed language list (languageController, LanguagesAdmin panel); the specific languages and translated strings are not listed in the digest. No RTL support is evidenced
- Browser support
- Modern evergreen browsers; no explicit browser matrix in the digest
| Minimum | Recommended | |
|---|---|---|
| CPU | 2 vCPU | 2vCPU |
| RAM | 2 GB (estimate for Node backend plus MongoDB connection) | 4 GB(estimate) |
| OS | Linux, macOS or Windows with Node.js 20.9 or later, npm, and a reachable MongoDB instance | Linux, macOS or Windows with Node.js 20.9 or later, npm, and a reachable MongoDB instance |
| Est. monthly hosting | $20 | $20 |
```bash
git clone <your-repo-url> swiftcart && cd swiftcart
npm install && npm --prefix backend install
cp .env.example .env.local && cp backend/.env.example backend/.env
# set MONGO_URI, JWT_SECRET, JWT_REFRESH_SECRET in backend/.env
npm --prefix backend run db:init
npm --prefix backend run seed:admin
npm run build
npm --prefix backend start &
npm start
```
```bash
# Frontend: import the repo in Vercel, set BACKEND_API_URL=https://<your-api>/api
# Backend: create a Render Web Service with Root Directory = backend
#   Build command: npm install
#   Start command: npm start
# Set MONGO_URI, JWT_SECRET, JWT_REFRESH_SECRET, FRONTEND_URL in Render
npm --prefix backend run db:init   # run once against the Atlas URI
```
```bash
cd swiftcart
# Claude Code reads CLAUDE.md for the project commands
npm install && npm --prefix backend install
npm run dev            # frontend :3001, backend :5000
npm --prefix backend test
```
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (3 minor)
Well-organized layers, but several oversized files and repeated demo/password logic; authz cannot be fully verified: route files not visible; demo-login admin bypass is a risk; mongoose-only access looks sound; limited visibility into most controllers and some gaps in schema/rules; lockfiles present, caret ranges throughout; a few risky or deprecated packages, no confirmed critical cve. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.