 Built by
About this software
About Hostinkar - Web Hosting, Domain & Billing Platform
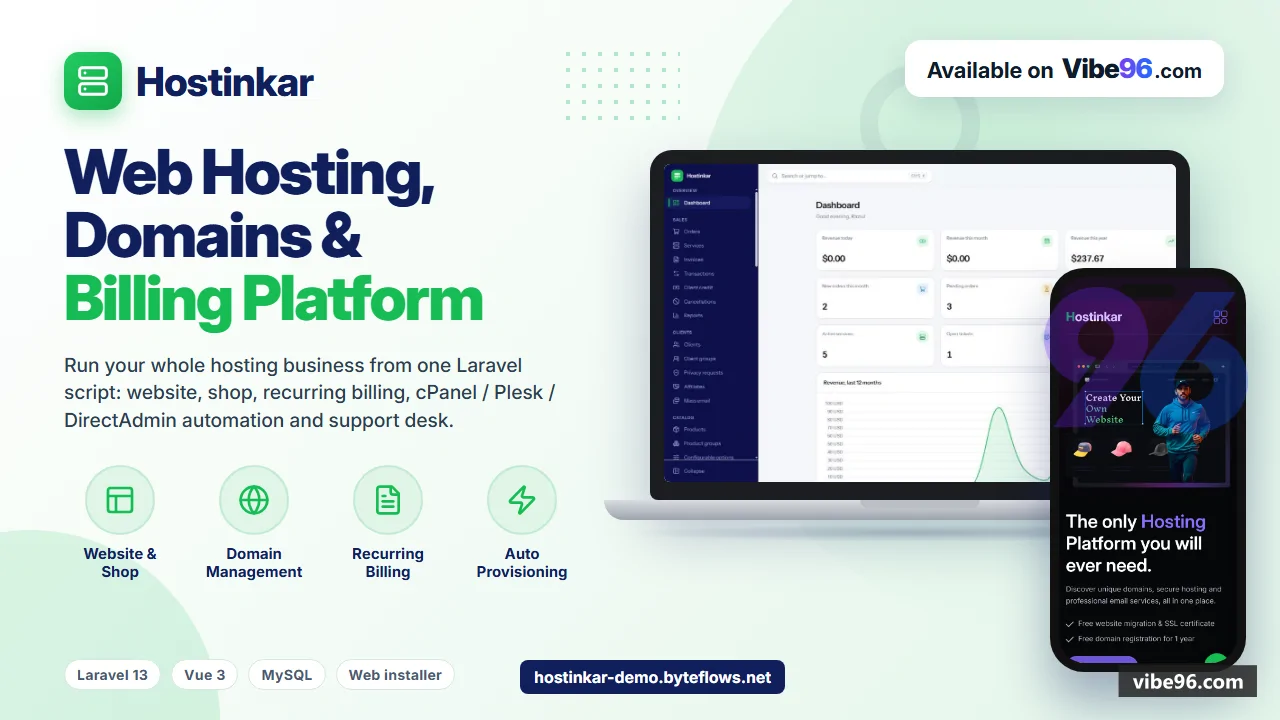
Hostinkar runs a complete web hosting business from one install. It includes a public website with a page builder, a shop for hosting plans and domains, recurring invoicing, and automatic account setup on cPanel/WHM, Plesk, and DirectAdmin. Clients get their own area for services, domains, invoices, and support tickets, and staff manage everything from a modern admin panel.
Payments: Stripe, PayPal, Razorpay, Paddle, SSLCommerz, bank transfer, and account credit. Domains: live search plus registration through Namecheap and ResellerClub. Support: tickets with departments, SLA timers, canned replies, and email piping. Optional AI tools work with your own OpenAI, Anthropic, Gemini, or OpenRouter key.
Built with Laravel 13, MySQL/MariaDB, Vue 3, TypeScript, and Inertia. A web installer sets everything up, so it also runs on shared cPanel hosting. Payment gateways, server modules, registrars, and AI providers are pluggable drivers, so you can add new ones without touching other code. It includes a Pest test suite, a documented REST API with an OpenAPI spec, Docker files, and an optional multi-tenant SaaS edition that is off by default.
Why Hostinkar - Web Hosting, Domain & Billing Platform
What makes it better
than the alternatives
- 01
Hosting-specific provisioning
Server modules for cPanel, Plesk, DirectAdmin and Manual, with failed actions retried through a module queue and listed under System → Automation.
- 02
Wide gateway coverage
Drivers for Stripe, Stripe Connect, PayPal, Razorpay, Paddle, SSLCommerz, bank transfer and account credit.
- 03
Website included
Blade public site with 36-section page builder, blog, knowledge base, menus, sitemap and multilingual/RTL support, not just a billing back end.
- 04
Built-in AI tools
OpenAI, Anthropic, Gemini and OpenRouter drivers power a support assistant, ticket assistant, plan recommender, domain generator, fraud check, content writer and translator.
- 05
Security and audit posture
Staff and client two-factor auth, passkeys, per-route permission middleware, encrypted gateway credentials, login logs and an activity log.
Billing
- Recurring invoices
- reminders
- late fees and PDF invoices
- Coupons
- tax rules
- EU VAT
- setup fees and client credit
- Upgrades/downgrades with proration and cancellation requests
- Transactions
- refunds and billing reports
Catalog & Shop
- Products
- product groups
- prices and billing cycles
- Configurable options (dropdown
- radio
- yes/no
- quantity)
- Cart and checkout with hosting and domain bundles
- Multi-currency display with exchange-rate updates
Domains
- Availability search via RDAP
- WHOIS and DNS lookups
- Namecheap and ResellerClub registrar drivers
- TLD pricing and domain search reports
- Client nameserver
- auto-renew
- lock and EPP code management
Provisioning
- Create
- suspend
- unsuspend and terminate accounts on cPanel
- Plesk
- DirectAdmin
- Suspension on non-payment and usage sync
- Single sign-on to the control panel
- Queued actions with retries
Client Area
- Dashboard
- services
- domains
- invoices and payment methods
- Tickets
- contacts and sub-users
- Two-factor
- passkeys and Google sign-in
- GDPR data export and erasure requests
- affiliates
Support Desk
- Departments
- priorities
- assignment and SLA timers
- Internal notes and canned replies
- Email piping into tickets
CMS
- Page builder
- menus
- blog and knowledge base
- Theme
- colours
- fonts and logo from admin
- SEO meta tags
- sitemap and robots.txt
Admin & API
- Staff roles and permissions via spatie/laravel-permission
- Global search across clients
- invoices
- orders
- tickets and staff
- Table lists with search
- filters
- bulk actions and CSV export
- REST API v1 with ability-scoped tokens and OpenAPI docs
AI
- Provider settings and usage metering
- Knowledge index with embeddings for the assistant
- Business insights and order fraud checks
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| PHP | — | — | Web, API | 53.3% |
| Vue | — | — | Front-end | 33.2% |
| CSS | — | — | Styling | 10.5% |
| TypeScript | — | — | Front-end | 1.5% |
| SQL | — | — | Database | 1.2% |
| JavaScript | — | — | Front-end | 0.3% |
- Primary language
- PHP 8.3+ with TypeScript (Vue 3)
- Framework
- Laravel 13 with Inertia 3 and Vue 3
- Database
- MySQL 8 / MariaDB 10.6+
- Authentication
- Session login via Fortify with 2FA (TOTP), passkeys, Google sign-in for clients, staff roles via spatie/laravel-permission, and API bearer tokens
- Licence
- Single-site
- Screens
- 150
- Database tables
- 80
- Supported languages
- Multilingual via JSON lang files with RTL support
- Browser support
- Modern evergreen browsers (Vue 3 SPA built by Vite); no explicit browser matrix in the digest
| Minimum | Recommended | |
|---|---|---|
| CPU | 2 vCPU | 4 vCPU |
| RAM | 4 GB | 8 GB |
| OS | Linux with PHP 8.3+ (8.4 recommended), Node.js 20.19+ for the build, MySQL 8 or MariaDB 10.6+ | Linux with PHP 8.3+ (8.4 recommended), Node.js 20.19+ for the build, MySQL 8 or MariaDB 10.6+ |
| Est. monthly hosting | $25 | $25 |
```bash
cp "Laravel Project/.env.example" "Laravel Project/.env"
# set DB_PASSWORD, DB_ROOT_PASSWORD and SITE_ADDRESS in .env
docker compose up -d
```
```bash
cd "Laravel Project"
composer install --no-dev --optimize-autoloader
npm ci && npm run build
cp .env.example .env && php artisan key:generate
# fill DB_* in .env, then:
php artisan migrate --force
```

Open /install to finish the web installer, or run `php artisan db:seed --class=AdminUserSeeder --force` after setting HOSTINKAR_ADMIN_EMAIL and HOSTINKAR_ADMIN_PASSWORD.
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (4 minor)
No real credentials found; shipped demo logins and a truncated xsrf cookie are the only concerns; authz design looks sound, but routes and policies were not visible, so coverage is unverified; manifests present but lockfiles and most dependency versions could not be verified from the digest; build mostly reproducible; setup doc and a few manifest details could not be fully verified; eloquent used throughout; db layer largely unverified, no injection seen, schema.sql not reviewable. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.