Why Jackpot
What makes it better
than the alternatives
- 01
Cryptographically random draw engine
Winners are selected with System.Security.Cryptography.RandomNumberGenerator, auditable in the admin panel
- 02
Multi-country pricing and prizes
Campaigns support per-country prices, currencies (AED, INR, SAR) and prize lists, with city-level member addresses
- 03
Wallet system with top-up and credit
Members can load funds via Stripe, use wallet balance at checkout, and receive refunds or credits from the operator
- 04
Demo payment mode
Test the entire checkout flow with Stripe-style test cards (no real Stripe account needed) before going live
- 05
Single-transaction checkout
Cart validation, payment verification, ticket allocation and wallet debit happen in one SQL transaction to prevent overselling
Mobile App (Flutter)
- Animated splash screen
- country selector (prices and currency follow the choice)
- Campaign browsing: running
- closing soon
- coming soon
- popular
- sold out; prize details
- countdown
- sold progress
- Guest cart that merges into the account at sign-in; wishlist
- Checkout with wallet or card (Stripe Payment Sheet)
- option to donate the product
- Tickets
- orders
- wallet with top-up
- notifications inbox
- Sign up
- sign in
- password reset by emailed code
- profile
- addresses
- delete account
- Contact us (messages reach admin panel)
- FAQ
- how it works
- terms and privacy pages loaded from server
- Colours and branding set from admin panel (light or dark theme)
- loaded at start-up
Admin Panel (Web)
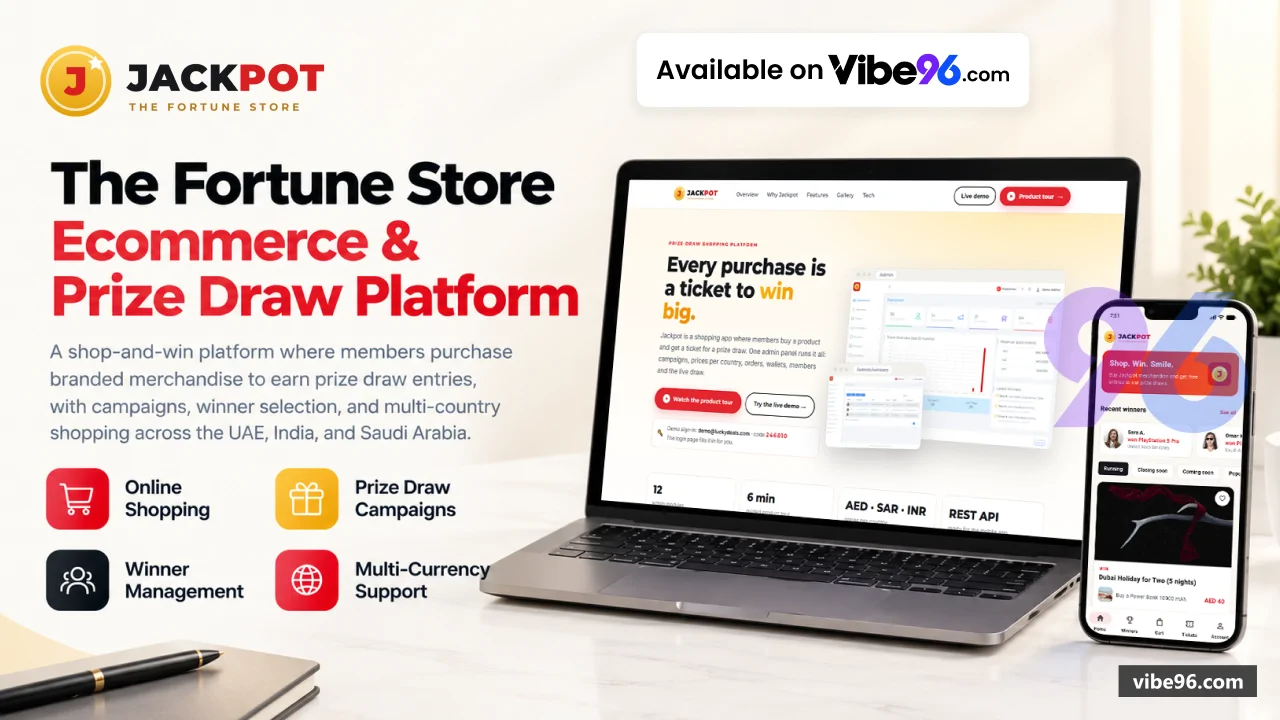
- Dashboard: totals
- 12-month ticket chart
- revenue per currency
- recent orders and winners
- Campaigns with per-country prices and prizes
- Arabic text
- images
- ticket lists and Draw winners button
- Products
- categories
- winners
- members (wallet credit
- enable/disable)
- orders (status changes)
- Reports: sales
- campaigns
- members
- wallet by
day/week/monthand by country; export to CSV - Excel or print
- Notifications to one member or everyone; member queries (contact messages); website and app pages with rich-text editor
- Admin users; settings for countries
- currencies
- cities
- Appearance settings: colours
- font
- logo
- title
- app colours (JSON theme loaded by mobile app)
- Email (SMTP) and Payments (Stripe keys or demo mode) configuration
- Data reset button (wipes all data
- reloads demo data from
database/seed.sql - Built-in product tour; optional public live demo sign-in for showcase servers
REST API
- Versioned JSON API (/api/v1) for mobile app
- /api/admin for integrations
- JWT authentication for members and admins (separate roles)
- tokens issued by AuthService
- ProblemDetails errors
- request validation with FluentValidation
- rate limiting on auth endpoints
- Interactive API reference at /scalar
- OpenAPI spec at /
openapi/v1.json - Endpoints: Store (public campaigns
- products)
- Account (member profile
- orders
- wallet
- tickets)
- Admin (campaigns
- members
- orders
- reports
- settings)
- Website (HTML pages)
Catalog & Campaigns
- Campaigns with status (Draft
- Active
- Closed
- Drawn)
- start/end dates
- ticket limit
- per-country prices and prizes
- Products with images
- categories
- stock tracking
- per-country prices
- Campaign prizes: product
- quantity
- winner count
- per-country assignment
- Arabic text support for campaign and product descriptions
- Campaign ticket lists: all tickets
- winners
- member tickets
- Sold-out detection
- closing-soon countdown
- coming-soon display
Sales & Checkout
- Cart: guest cart (by GuestId)
- member cart
- merge guest cart at sign-in
- Checkout: wallet balance
- Stripe card payment (Payment Intent)
- demo card payments (test mode)
- Order creation in one SQL transaction: validate cart
- verify payment
- allocate tickets
- debit wallet
- clear cart
- Order statuses: Pending
- Confirmed
- Cancelled
- Refunded
- Ticket allocation: one ticket per product unit
- linked to order and member
- Wallet top-up via Stripe or demo payment
- wallet credit by admin
- refunds to wallet
Member Management
- Member registration with email
- password (PBKDF2-SHA512)
- country
- city
- optional phone and gender
- Sign-in with email and password
- JWT token issued (30-day expiry for members)
- Password reset: emailed 6-digit OTP (15-minute expiry)
- hashed in database
- Profile: first name
- last name
- phone
- gender
- country
- city
- Addresses: multiple addresses per member
- default address flag
- Member status: Active
- Disabled (admin can disable accounts)
- Device ID tracking for push notifications (not yet implemented)
- Delete account: member can request deletion (not implemented in admin panel)
Draws & Winners
- Draw winners button in admin panel (campaign must be Closed)
- Cryptographically random selection: System.Security.Cryptography.RandomNumberGenerator.GetInt32
- One winner per prize
- no duplicates within a campaign
- Winner records: member
- campaign
- prize
- ticket number
- draw date
- Winners list in admin panel and mobile app
- Campaign status changes to Drawn after draw completes
Reports & Analytics
- Sales report: revenue
- orders
- tickets by
day/week/monthand by country; bar chart - export to CSV/Excel
- Campaigns report: tickets sold
- revenue
- winners by campaign and by country
- Members report: new members
- total members by
day/week/monthand by country - Wallet report: top-ups
- credits
- debits
- balance by
day/week/monthand by country - Dashboard: 12-month ticket chart
- revenue per currency
- recent orders and winners
Integrations & Settings
- Email (SMTP): host
- port
- username
- password (encrypted with Data Protection)
- from address
- from name
- Stripe: secret key (encrypted)
- publishable key (sent to mobile app with each payment)
- Demo payments: test mode with Stripe-style test cards (4242 4242 4242 4242
- etc.)
- no real Stripe account needed
- Countries
- currencies
- cities: admin can
add/edit/delete - Appearance: primary colour
- secondary colour
- font
- logo
- title
- app theme JSON (loaded by mobile app)
- Data reset: wipes all data except settings
- reruns
database/seed.sql(optional - disabled by default)
Security & Infrastructure
- JWT tokens: HS256
- configurable signing key
- separate expiry for members (30 days) and admins (8 hours)
- Password hashing: PBKDF2-SHA512
- 100
- 000 iterations
- 32-byte salt
- Role-based access: Member policy for /
api/v1/meand /api/v1/checkout - Admin policy for /api/admin and /admin
- Rate limiting: 20 requests per minute on auth endpoints (sign-in
- registration
- password reset
- contact)
- SQL injection prevention: hand-written SQL with Dapper parameters only
- no concatenation
- Payment verification: amount
- currency
- owner
- purpose checked on server; each Payment Intent used once
- Secrets encrypted: SMTP password and Stripe secret key stored encrypted with Data Protection
- Database initialization: creates database and runs schema.sql and seed.sql on first start (optional)
- Health checks: /health endpoint with database connectivity check
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| CSS | — | — | Styling | 48.8% |
| JavaScript | — | — | Front-end | 26.3% |
| SCSS | — | — | Styling | 8.3% |
| C# | — | — | Web, API, admin | 6% |
| Dart | — | — | Mobile app | 4.6% |
| HTML | — | — | Front-end | 2.9% |
| C# (Razor) | — | — | Web pages | 2.5% |
| SQL | — | — | Database | 0.6% |
| Swift | — | — | Mobile app | 0.1% |
| Java | — | — | API | 0% |
| Python | — | — | Web, API | 0% |
| Shell | — | — | Scripts | 0% |
| Kotlin | — | — | Mobile app | 0% |
- Primary language
- C# 12 / .NET 10
- Framework
- ASP.NET Core 10 (MVC + Minimal API)
- Database
- SQL Server 2019+
- Authentication
- JWT (API) + Cookie (Admin)
- Licence
- Single-site
- Screens
- 47
- Database tables
- 23
- Supported languages
- English only (Arabic text fields supported)
- Browser support
- Modern browsers (ES6+)
| Minimum | Recommended | |
|---|---|---|
| CPU | 2 vCPU | 4 vCPU |
| RAM | 4 GB RAM / 20 GB disk | 8 GB RAM / 40 GB disk |
| OS | Linux (Docker) or Windows Server 2019+ (IIS), .NET 10 runtime, SQL Server 2019+ | Linux (Docker) or Windows Server 2019+ (IIS), .NET 10 runtime, SQL Server 2019+ |
| Est. monthly hosting | $25 | $25 |
```bash
cp .env.example .env
# Edit .env: set DB_PASSWORD (8+ chars, upper/lower/digit/symbol) and JWT_SIGNING_KEY (32+ random chars)
docker compose up -d --build
# Open http://localhost:8080/admin (admin / Admin@123)
```
```bash
sudo apt update && sudo apt install -y dotnet-sdk-10.0 mssql-server mssql-tools18
sudo /opt/mssql/bin/mssql-conf setup  # Choose Express, set SA password
cd "NET Project"
dotnet restore
dotnet publish src/LuckyDeals.Web/LuckyDeals.Web.csproj -c Release -o /var/www/jackpot
# Edit /var/www/jackpot/appsettings.json: set ConnectionStrings__Default and Jwt__SigningKey
sudo systemctl enable --now jackpot.service  # Create systemd unit first
# Configure Nginx reverse proxy to port 5000
```
```powershell
# Install .NET 10 Hosting Bundle from https://dotnet.microsoft.com/download
# Install SQL Server 2019+ Express
cd "NET Project"
dotnet publish src\LuckyDeals.Web\LuckyDeals.Web.csproj -c Release -o C:\inetpub\jackpot
# In IIS Manager: create site, point to C:\inetpub\jackpot, set app pool to "No Managed Code"
# Edit C:\inetpub\jackpot\web.config: add <environmentVariable name="ConnectionStrings__Default" value="Server=.;Database=LuckyDeals;User Id=<user>;Password=<password>;TrustServerCertificate=True" />
# Add JWT_SIGNING_KEY environment variable (32+ random chars)
```
```bash
# Start SQL Server in Docker
docker run -e "ACCEPT_EULA=Y" -e "MSSQL_SA_PASSWORD=YourStrong@Passw0rd" -p 1433:1433 -d mcr.microsoft.com/mssql/server:2022-latest
cd "NET Project"
export ConnectionStrings__Default="Server=localhost;Database=LuckyDeals;User Id=sa;Password=YourStrong@Passw0rd;TrustServerCertificate=True"
export Jwt__SigningKey="$(openssl rand -base64 48)"
dotnet run --project src/LuckyDeals.Web --urls http://localhost:5080
# Open http://localhost:5080/admin
```
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (4 minor)
Dependencies mostly current; flutter packages slightly outdated, no critical vulnerabilities; weak default admin password and example secrets need attention before production; strong authentication and role checks; minor ownership gaps on read endpoints; moderate code duplication and some oversized files; structure generally sound but needs refactoring. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.