 Built by
About this software
About Resturant management system
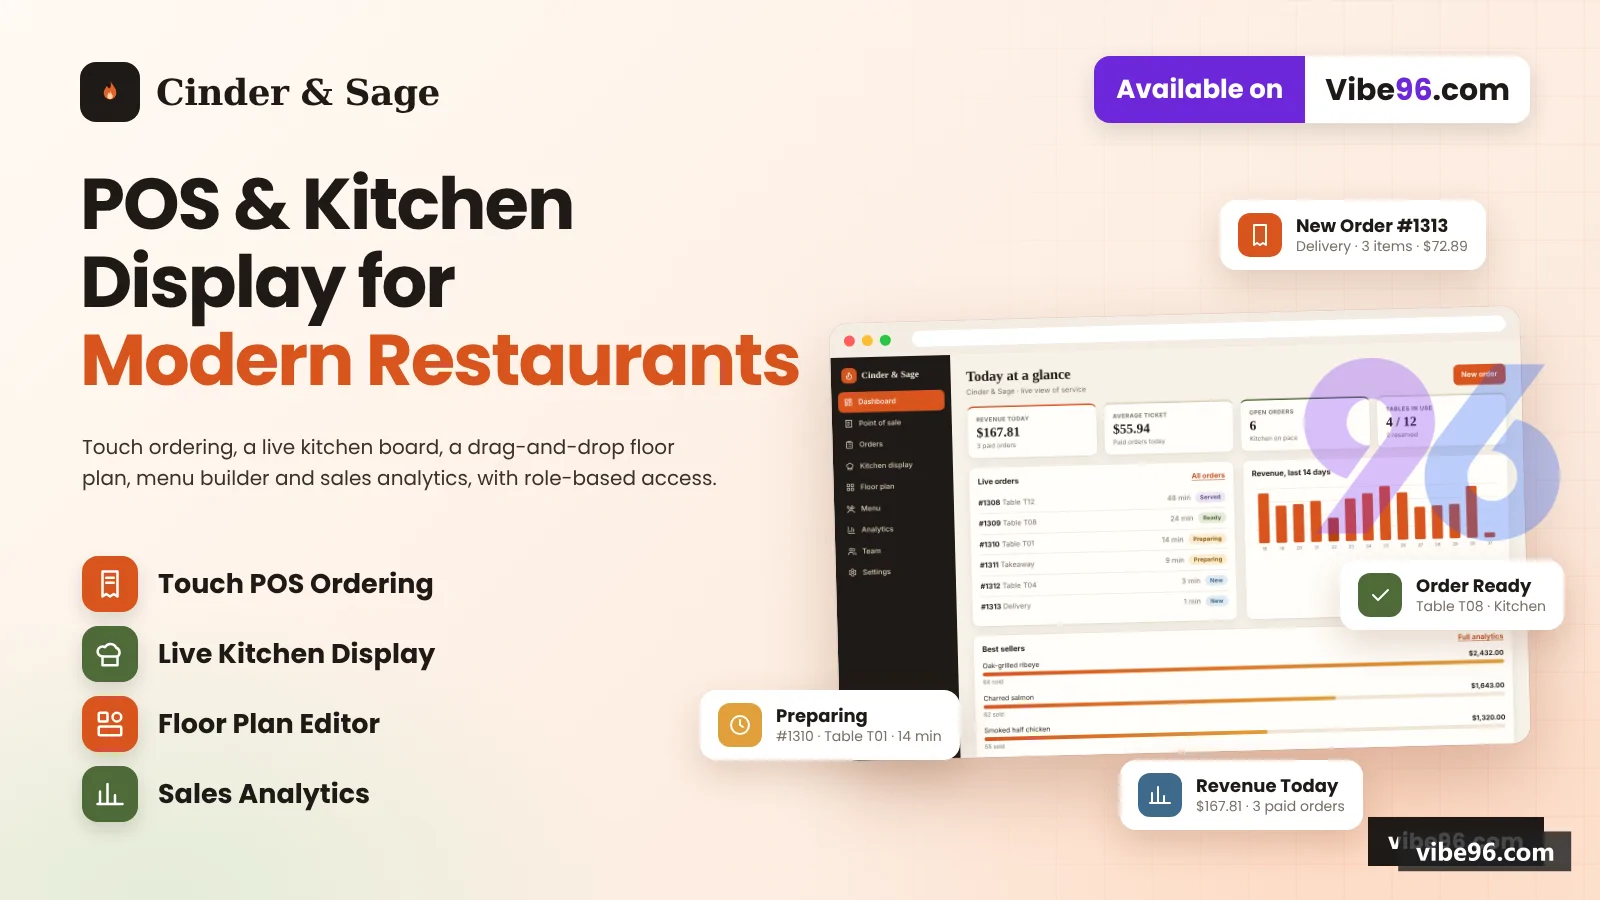
Cinder & Sage is a restaurant operations app built with Next.js 15, React 19, TypeScript and Supabase (PostgreSQL, Auth, Realtime). It covers touch POS ordering, a kitchen display board, a drag-and-drop floor-plan editor, a menu builder, sales analytics, team roles and settings, across nine workspace screens plus a landing page and a login page. Four roles (Owner, Manager, Staff, Kitchen) are enforced in the database through row-level security and SECURITY DEFINER functions, not just hidden buttons. Stripe Checkout with a signature-verified webhook is optional, and cash or card-terminal payments can be recorded. Without Supabase configured, it runs as a browser-only demo with fictional data. It ships with a Dockerfile, docker-compose, SQL schema and seed data, and a GitHub Actions quality workflow. The README states 105 database RLS/role checks, but those tests were not run for this listing.
Why Resturant management system
What makes it better
than the alternatives
- 01
Database-enforced authorization
Row Level Security and SECURITY DEFINER functions re-check the caller's role on every order, payment and layout change.
- 02
Live kitchen board
The KDS moves orders through New, Preparing, Ready and Served via Supabase Realtime, with a 30-second polling fallback.
- 03
Server-side money maths
Totals, tax and service charge are computed in SQL numeric, with a mirrored rules.ts used by the demo store.
- 04
Runs with or without a backend
A single DataStore interface has a browser-only demo implementation and a Supabase implementation.
- 05
Built-in quality gates
Typecheck, structural and secret scans, lint, a DB test script and a CI workflow are included, plus Docker deployment.
Point of Sale
- Touch menu grid and cart with order notes
- Dine-in
- takeaway and delivery order types
- Table picker
- Tax and service charge applied from settings
Kitchen Display
- Board with New
- Preparing
- Ready and Served stages
- Realtime updates with polling fallback
- Visible to Owner
- Manager
- Staff and Kitchen roles
Floor Plan
- Drag-and-drop layout editor
- Round
- square and long tables with seats and labels
- Live table status colours and one-click status changes
Menu Builder
- Categories and dishes with prices
- descriptions and emoji
- Availability toggle
- Archive instead of delete
Orders & Payments
- Order list with search and filters
- Record cash or card-terminal payments
- Optional Stripe Checkout with signed webhook
Analytics & Dashboard
- Daily revenue and best sellers
- Sales by category and orders by hour
- Payment-method mix
Team & Settings
- Owner
- Manager
- Staff and Kitchen roles
- Last active owner cannot be removed
- Restaurant name
- currency
- timezone
- tax rate
- service charge and contact details
Deployment & Demo
- Dockerfile and docker-compose with health check
- SQL schema
- seed data and first-admin script
- Marketing landing page and no-password demo workspace
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| TypeScript (React) | — | — | Front-end | 40% |
| TypeScript | — | — | Front-end | 30.3% |
| SQL | — | — | Database | 24.8% |
| CSS | — | — | Styling | 4.1% |
| PowerShell | — | — | Scripts | 0.7% |
- Primary language
- TypeScript 5.9 (strict) on Node.js 20.9+
- Framework
- Next.js 15.5 (App Router) with React 19.1
- Database
- PostgreSQL via Supabase (RLS, SECURITY DEFINER functions, Realtime); minimum version not pinned in digest
- Authentication
- Supabase Auth email and password, cookie session via @supabase/ssr, role checks in Postgres RLS and route handlers
- Licence
- Single-site
- Screens
- 11
- Database tables
- 8
- Supported languages
- English UI only; no i18n framework evident; no RTL support
- Browser support
- Modern evergreen browsers (Chrome, Edge, Firefox, Safari); touch-friendly POS layout
| Minimum | Recommended | |
|---|---|---|
| CPU | 1 vCPU | 2 vCPU |
| RAM | 1 GB RAM | 2 GB RAM |
| OS | Linux container (node:22-alpine) or any OS with Node.js 20.9+ and npm 10+ | Linux container (node:22-alpine) or any OS with Node.js 20.9+ and npm 10+ |
| Est. monthly hosting | $25 | $25 |
```
cp .env.example .env
docker compose up -d --build
```
Open http://localhost:3000 and check http://localhost:3000/api/health.
```
cd "Node-Project"
cp .env.example .env.local
npm install
npm run build
npm run start
```
Put a reverse proxy with TLS in front of port 3000.
A netlify.toml is included in Node-Project/. Set the NEXT_PUBLIC_* variables and server-only secrets in the host's dashboard, then build with:
```
npm run build
```
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (5 minor)
No real credentials found; one shipped demo password and a documented demo login are weak defaults; layered structure is clear, but several files and checks are hard-coded or mix concerns; mostly reproducible next.js build; setup doc unseen and a few coherence gaps remain; database layer looks well designed, but schema, supabase-store and rls tests were not provided, so it can't be fully verified; authz is well-designed (rls + role checks) but key routes and the sql boundary could not be verified. None of these stop the software from working; the developer has been told and improvements come in a future update.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.