 Built by
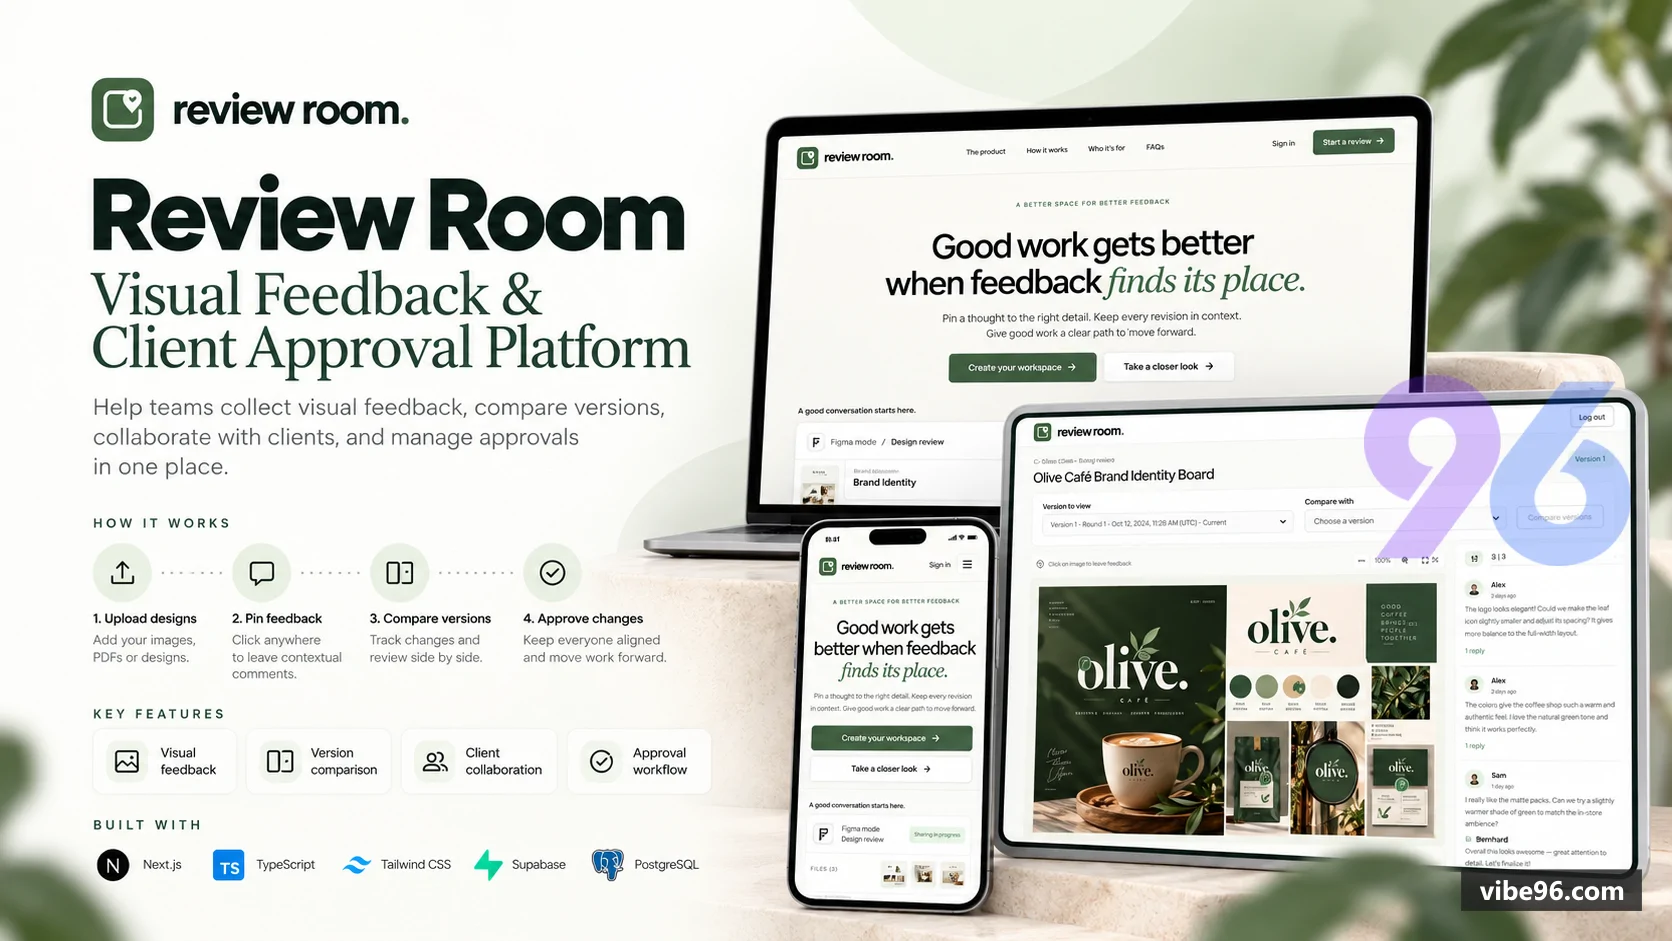
Why Review Room – Visual Feedback & Client Approval SaaS
What makes it better
than the alternatives
- 01
Coordinate-pinned feedback
Comments attach to specific image coordinates and persist across versions, eliminating ambiguous 'change this' requests.
- 02
Version-locked decisions
Each client approval or change request belongs to one immutable version, requiring fresh review after revisions.
- 03
Isolated guest demo
24-Hour sessions with three fictional projects let visitors test Designer/Client workflows without affecting real workspaces.
- 04
Private Supabase Storage
All uploads use authenticated bucket access with PostgreSQL RLS; no public URLs or CDN exposure.
- 05
Durable network quotas
HMAC-signed rate limits survive restarts and prevent signup abuse without Redis or external state.
Authentication & Identity
- Email/password signup with instant account creation (no confirmation emails)
- Google OAuth integration with verified identity matching for invitations
- Cookie-based sessions via Supabase Auth
- Network-based signup rate limiting with HMAC-signed buckets
- Automatic workspace bootstrap on first signup
Workspace & Project Management
- Multi-tenant workspaces with
Owner/Designer/Clientroles - Project creation and archiving
- Role-based project visibility (Owners see all
- others see assigned projects)
- Project member assignment and removal
- Activity feed with per-user unread tracking
Asset Upload & Versioning
JPG/PNG/WebPupload to private Supabase Storage bucket- Automatic version creation preserving earlier files and feedback
- Image preview generation with Sharp
- Version comparison side-by-side view
- Immutable version history with creation timestamps
Visual Feedback & Comments
- Coordinate-pinned comments on specific image details
- Threaded replies within comment discussions
- Resolve/reopen status for each comment thread
- Comment persistence across versions
- Real-time comment count and status indicators
Review & Approval Workflow
- Client-specific approval or change-request decisions per version
- Decision history tracking with timestamps
- Version-locked decisions requiring fresh review after revisions
- Designer/Client role enforcement for decision actions
- Approval status display on project overview
Invitations & Sharing
- Email-bound invitation links with verified Google identity matching
- Expiring read-only share links for single versions (24-hour default)
- Revocable share tokens with usage tracking
- Role assignment (Designer/Client) during invitation
- Share link access without authentication
Demo & Marketing
- Isolated 24-hour guest sessions with fictional projects
- Designer/Client view switching in demo mode
- Sample feedback reset without affecting real data
- Interactive homepage review preview (browser-only state)
- Three fictional design concepts with two versions each
Activity & Notifications
- Project activity feed with event descriptions
- Per-user unread position tracking
- Activity events for uploads
- comments
- decisions
- and invitations
- Workspace-scoped activity queries
- Timestamp-based event ordering
Maintenance & Operations
- Cron-triggered demo session cleanup (24-hour expiry)
- Orphaned upload cleanup with Storage reconciliation
- Bearer-authenticated maintenance endpoint
- PostgreSQL migration rehearsal script
- Integration test suite with isolated test database
Data & Permissions
- PostgreSQL with Prisma ORM and pg driver adapter
- Row-level security enforcing workspace/project membership
- Transaction-local identity for all authenticated queries
- Workspace-scoped data isolation
- Append-only migration strategy with validation
| Language | Version | Framework | Used for | Share of code |
|---|---|---|---|---|
| TypeScript | — | — | Front-end | 45% |
| CSS | — | — | Styling | 24% |
| TypeScript (React) | — | — | Front-end | 22.6% |
| SQL | — | — | Database | 7.8% |
| Python | — | — | Web, API | 0.6% |
- Primary language
- TypeScript 6.0.3
- Framework
- Next.js 16.4.2 (App Router), React 19.3.1
- Database
- PostgreSQL 14+
- Authentication
- Supabase Auth (email/password + Google OAuth)
- Licence
- Single-site
- Screens
- 18
- Database tables
- 16
- Supported languages
- English only
- Browser support
- Modern browsers (Chrome, Firefox, Safari, Edge); responsive 320px+
| Minimum | Recommended | |
|---|---|---|
| CPU | 2 vCPU | 2 vCPU |
| RAM | 2 GB | 4 GB |
| OS | Node.js 22.18.0+, Linux/macOS | Node.js 22.18.0+, Linux/macOS |
| Est. monthly hosting | $25 | $25 |
```bash
# Install Vercel CLI
npm i -g vercel

# Set environment variables in Vercel dashboard:
# NEXT_PUBLIC_APP_URL, NEXT_PUBLIC_SUPABASE_URL, NEXT_PUBLIC_SUPABASE_PUBLISHABLE_KEY,
# SUPABASE_SECRET_KEY, DATABASE_URL, DIRECT_URL, SUPABASE_DB_CA_CERT,
# SUPABASE_STORAGE_BUCKET, SIGNUP_RATE_LIMIT_SECRET, CRON_SECRET

# Deploy
vercel --prod

# Run migrations
pnpm db:deploy
```
```bash
# Copy environment template
cp .env.example .env
# Edit .env with your Supabase credentials

# Install dependencies
pnpm install

# Generate Prisma client
pnpm db:generate

# Run migrations
pnpm db:deploy

# Build and start
pnpm build
pnpm start
```
```bash
# Install pnpm 11.21.0
npm install -g pnpm@11.21.0

# Install dependencies
pnpm install

# Copy .env.example to .env and configure Supabase credentials
cp .env.example .env

# Generate Prisma client
pnpm db:generate

# Run migrations
pnpm db:deploy

# Start development server
pnpm dev
# Visit http://localhost:3000
```
Quality report
Manually reviewedHow to read the quality report
What this is. Every project on Vibe96 goes through an automated audit of its source code before a reviewer in Dubai checks it by hand. The score is out of 100; 75 is the minimum to be listed, and any single failing check blocks a listing regardless of the score.
- Security
- No real credentials in the code, every data-changing route protected, admin areas role-gated, no SQL built from user input.
- Code structure
- A developer can navigate and extend it: clear module boundaries, no giant files, little copy-paste.
- Docs & completeness
- The setup guide, example config, schema and required files the builder committed to are actually in the archive.
- Dependency health
- Packages pinned, no known critical vulnerabilities, no abandoned libraries in production paths.
- Build & deploy
- A clean machine can restore, build and start it by following the shipped instructions.
Warnings are problems that didn't block the listing; they stay visible here until a later version clears them. The audit reads the code — it does not run it — so always try the live demo before you buy. Lines of code are counted from the same audited archive.
Reviewer notes (1 minor)
Small improvements the developer has been told about. None of them stop the software from working.
Versions & updates
No updates yet. New versions appear here with a changelog.
Buyers receive updates free for 1 year.
What you get
- </>Full source codeThe complete audited source, delivered as a download from your account. No obfuscation.
- ▤DocumentationSetup guide, architecture notes, CLAUDE.md and AGENTS.md.
- ↻One year of updatesEvery new version the builder publishes, free for 12 months.
- ♧30 days of supportInstallation and defect support through Vibe96 tickets.