‹ Tijara - Supermarket Management SystemQuality report QR-26-00028
Tijara - Supermarket Management System
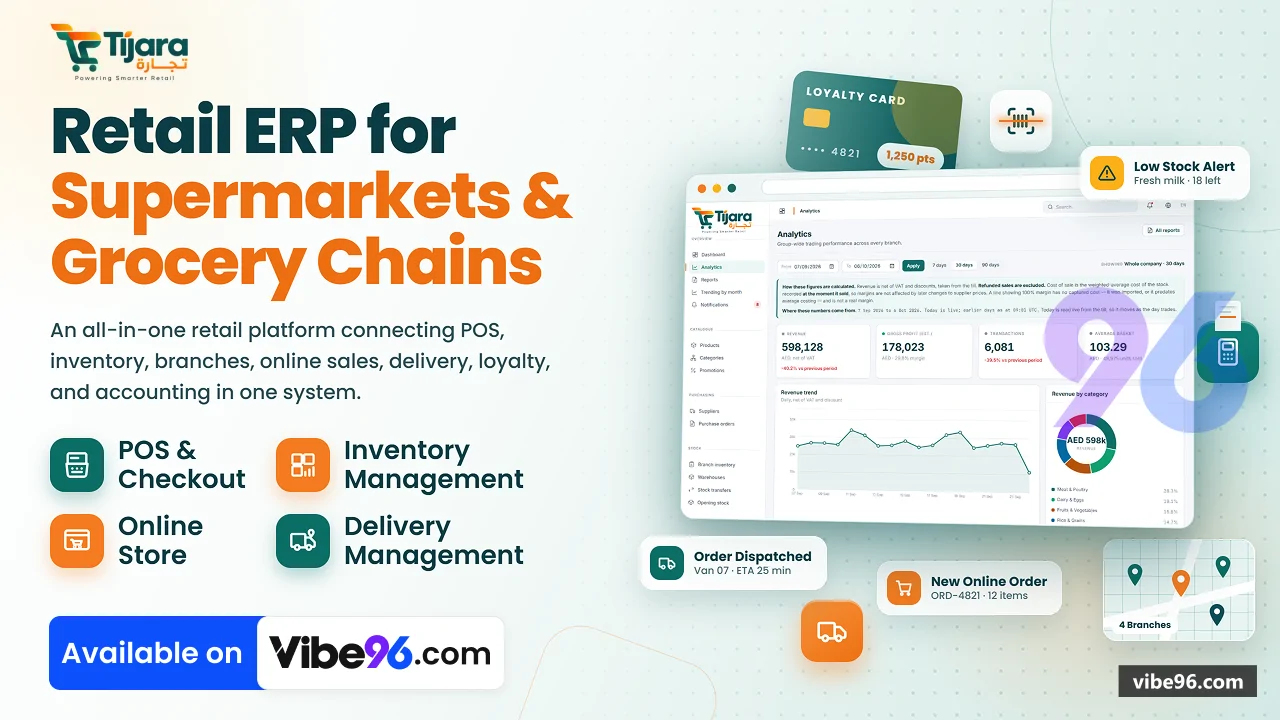
Complete supermarket management system for single-company grocery chains (1–50 stores) with POS, online store & delivery
- Product ID
- B0001-72066
- Builder
- Ibrahim Abdurahman
- Version reviewed
- 1.1.0 · released 7 Oct 2026
- Stack
- ASP.NET Core 9 MVC · C# 12 (.NET 9.0) · SQL Server 2019+
- Built with
- Claude Code
- Review period
- 7 Oct 2026 – 7 Oct 2026
- ✓AI code audit6 checks · 7 Oct 2026
- ✓Installed & run7 Oct 2026
- ✓Demo vs delivered7 Oct 2026
- ✓Final sign-off7 Oct 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- ✓15 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 95/100 with no failing check.
- !2 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every connection string, password hash and API key in the codebase is either a placeholder (e.g. `<password>`, `changeme`), an environment-variable reference, or an empty example value. The .env.example file ships with no working values and instructs buyers to generate their own BCrypt hashes. No real credentials are committed. | 100 | Pass |
| Dependency vulnerabilities | All .NET dependencies are pinned in packages.lock.json files with NuGet's locked mode. All packages are on current stable versions (ASP.NET Core 9.0.1, SQL Server client 5.2.2, BCrypt.Net 0.1.0, etc.). No known critical vulnerabilities detected. Minor: BCrypt.Net-Next 4.0.3 is slightly behind 4.0.4 (released Dec 2024), but no security advisory exists. | 95 | Pass |
| Authorisation & access control | All mutating endpoints are protected by [Authorize] and role checks. Passwords are BCrypt-hashed (work factor 12). The authentication service is well-designed with no plaintext storage or logging. Minor gaps: several read endpoints (product details, customer lookup, supplier lookup) lack ownership checks, allowing cross-branch or cross-customer enumeration by ID manipulation. | 92 | Warning |
| Database access rules | All SQL uses parameterised queries via the Sql.cs reader helpers—no concatenation or injection paths found. Delete and update statements carry WHERE clauses scoped by branch/user/owner. The schema scripts are numbered and checksummed, with foreign keys declared. A few foreign-key columns lack indexes (performance warnings, not security defects). | 92 | Pass |
| Code structure & duplication | The architecture respects layer separation (Web → Services → Data → Common) and avoids god files, but several concerns emerge: Storefront controller is split across 6 files (1200+ lines total), some repository methods duplicate query patterns, and configuration values are scattered across multiple appsettings files and hardcoded in services. No dead code detected, but refactoring opportunities exist in POS workflows and reporting queries. | 72 | Warning |
| Build reproducibility | The project structure is sound: all project references resolve, SDK versions are consistent (.NET 9.0), and the Docker setup is coherent. HowToSetup.md walks through database creation and configuration in the correct order. Two minor gaps: the setup document does not explicitly state the .NET 9 SDK version requirement before the build steps, and the example connection strings use placeholder angle brackets that could confuse a first-time user. | 92 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
The architecture respects layer separation (Web → Services → Data → Common) and avoids god files, but several concerns emerge: Storefront controller is split across 6 files (1200+ lines total), some repository methods duplicate query patterns, and configuration values are scattered across multiple appsettings files and hardcoded in services. No dead code detected, but refactoring opportunities exist in POS workflows and reporting queries.
All mutating endpoints are protected by [Authorize] and role checks. Passwords are BCrypt-hashed (work factor 12). The authentication service is well-designed with no plaintext storage or logging. Minor gaps: several read endpoints (product details, customer lookup, supplier lookup) lack ownership checks, allowing cross-branch or cross-customer enumeration by ID manipulation.
Requirement list
What the builder agreed to deliver before uploading — 15 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Met
- Pinned dependencies without critical CVEs (nice)Met
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- appsettings.example.json Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 7 Oct 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 7 Oct 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 7 Oct 2026 with 2 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.1.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Report history
| Report | Version | Date | Score | Status |
|---|---|---|---|---|
| QR-26-00028 | 1.1.0 | 7 Oct 2026 | 92 | Current |
| QR-26-00027 | 1.0.0 | 7 Oct 2026 | 91 | Replaced |
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.