‹ MailFlowQuality report QR-26-00035
MailFlow
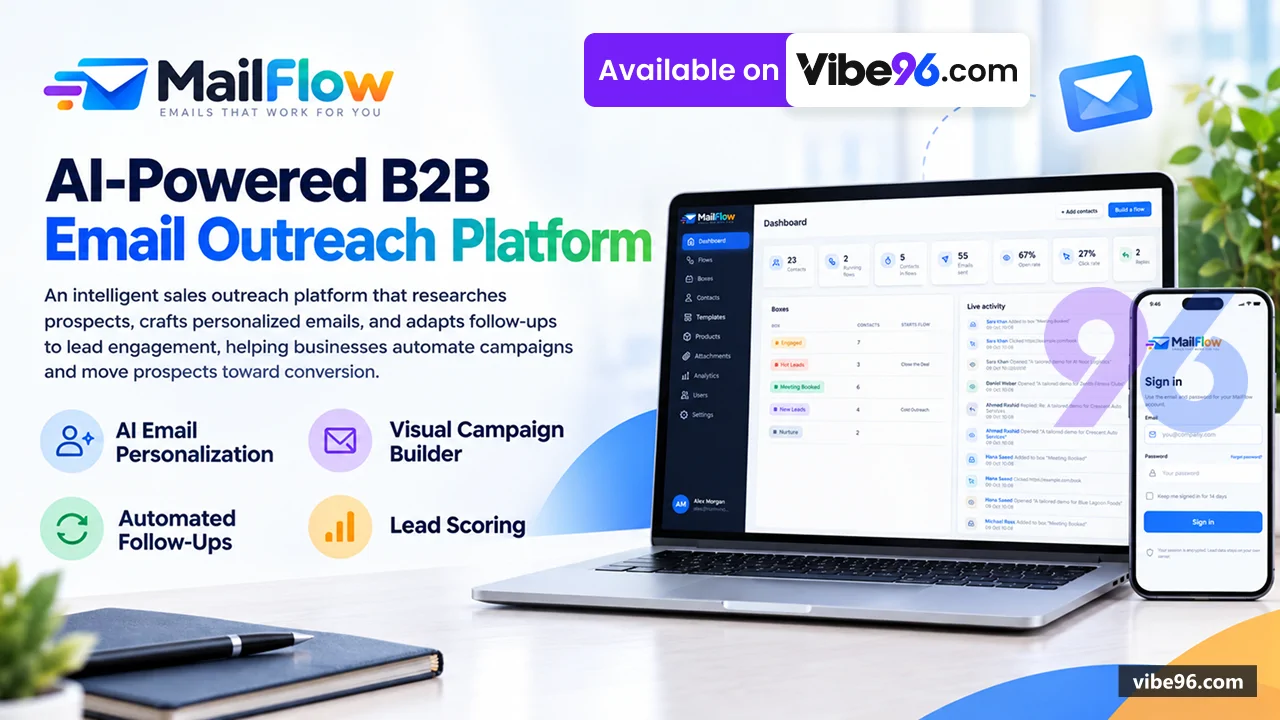
AI-personalised email lead generation with drag-and-drop flow builder
- Product ID
- B0004-49915
- Builder
- Ibrahim Abdurahman
- Version reviewed
- 1.0.0 · released 12 Oct 2026
- Stack
- ASP.NET Core 10 · C# 14 · SQL Server 2019
- Built with
- Claude Code
- Review period
- 9 Oct 2026 – 12 Oct 2026
- ✓AI code audit6 checks · 9 Oct 2026
- ✓Installed & run12 Oct 2026
- ✓Demo vs delivered12 Oct 2026
- ✓Final sign-off12 Oct 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !14 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 85/100 with no failing check.
- !3 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | No hardcoded API keys, database passwords, or other real secrets were found in the codebase. All configuration uses placeholders and environment variables correctly. However, the system generates a random admin password on first run if none is provided, which is logged in plaintext and could be overlooked in production deployments. | 92 | Warning |
| Dependency vulnerabilities | The project lacks a packages.lock.json lockfile, meaning dependency versions float on every restore. The MailFlow.csproj uses unpinned version ranges for all packages (e.g., "10.0.*"), which can pull in breaking changes or vulnerabilities without notice. No known critical vulnerabilities detected in the declared .NET 10 packages, but the absence of pinning is a deployment risk. | 85 | Warning |
| Authorisation & access control | Checked by our reviewers during the human review. | 70 | Warning |
| Database access rules | All queries use EF Core with parameterized statements; no raw SQL or string concatenation. Delete and update operations correctly scope to the current organization's data. The schema (a project file) is complete and re-runnable with proper foreign keys and cascade rules. Minor issue: several foreign key columns lack explicit indexes (SQL Server auto-indexes FK constraints only on the referenced side, not the referencing side). | 92 | Pass |
| Code structure & duplication | The project has clean module boundaries and good separation of concerns (Pages, Services, Engine, Endpoints). However, there is noticeable duplication in email/tracking logic, some configuration hard-coded in multiple places, and a few files approaching 400+ lines that could be split. No dead code detected, but refactoring would improve maintainability. | 78 | Warning |
| Build reproducibility | The project builds cleanly with .NET 10 SDK and SQL Server 2022. Docker Compose setup is complete and functional. HowToSetup.md is missing but README.md covers the essentials. Minor issues: appsettings.json contains a local connection string instead of using the example file, and the setup document doesn't explicitly list .NET 10 SDK as a prerequisite. | 92 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
No hardcoded API keys, database passwords, or other real secrets were found in the codebase. All configuration uses placeholders and environment variables correctly. However, the system generates a random admin password on first run if none is provided, which is logged in plaintext and could be overlooked in production deployments.
The project has clean module boundaries and good separation of concerns (Pages, Services, Engine, Endpoints). However, there is noticeable duplication in email/tracking logic, some configuration hard-coded in multiple places, and a few files approaching 400+ lines that could be split. No dead code detected, but refactoring would improve maintainability.
The project lacks a packages.lock.json lockfile, meaning dependency versions float on every restore. The MailFlow.csproj uses unpinned version ranges for all packages (e.g., "10.0.*"), which can pull in breaking changes or vulnerabilities without notice. No known critical vulnerabilities detected in the declared .NET 10 packages, but the absence of pinning is a deployment risk.
Requirement list
What the builder agreed to deliver before uploading — 14 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Met
- Pinned dependencies without critical CVEs (nice)Partial
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- appsettings.example.json Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 12 Oct 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 12 Oct 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 12 Oct 2026 with 3 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.