‹ Linkhive — ISP Billing, Customer Portal & MikroTik / RADIUS AutomationQuality report QR-26-00084
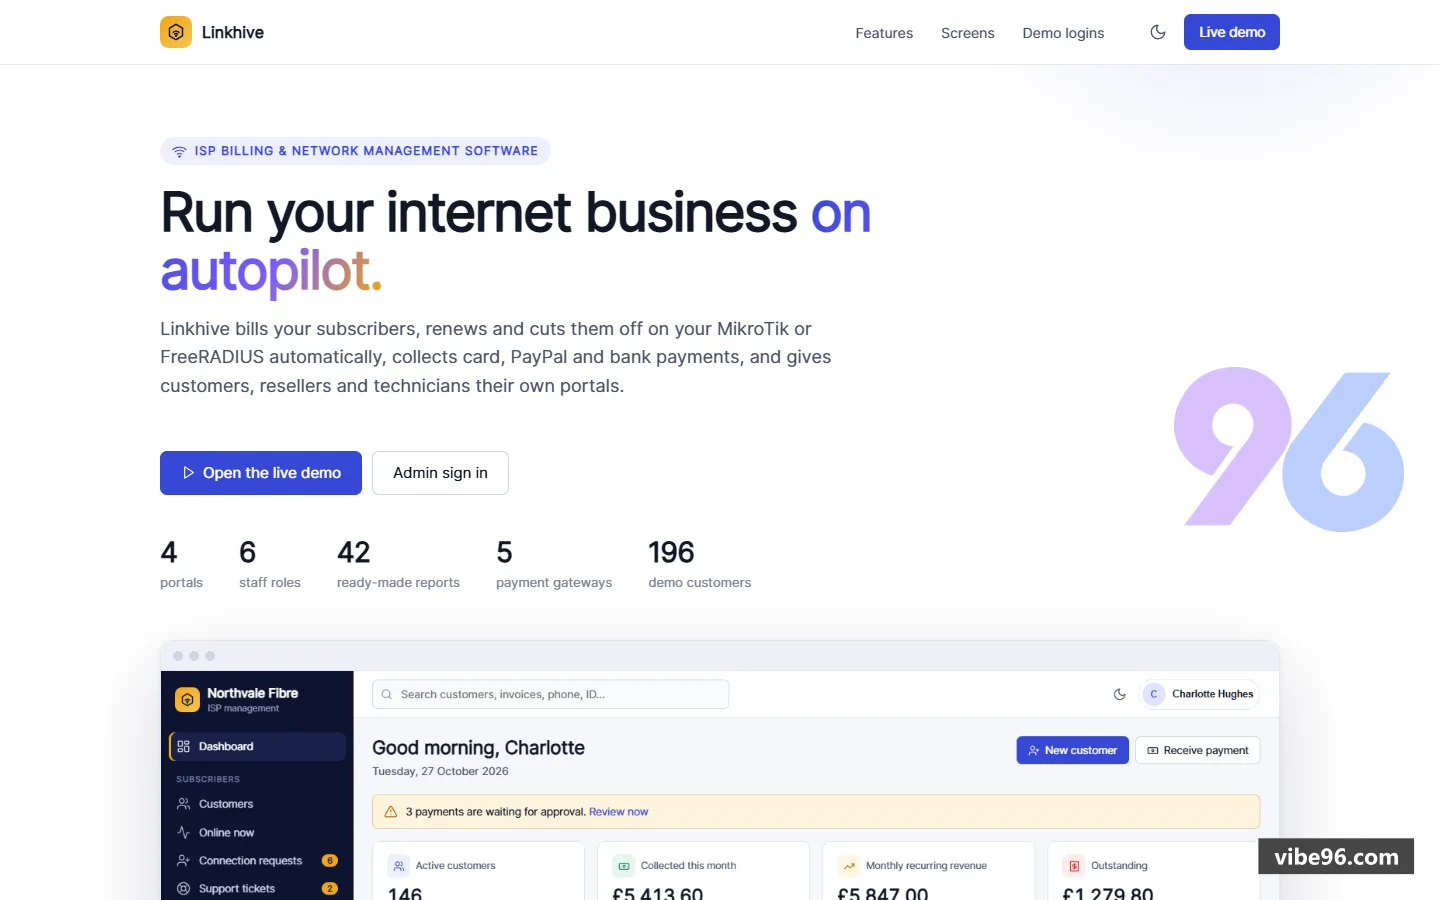
Linkhive — ISP Billing, Customer Portal & MikroTik / RADIUS Automation
Self-hosted ISP billing and MikroTik/RADIUS automation for broadband and Wi-Fi with customer and technician portals.
- Product ID
- B0264-81528
- Builder
- Ahsan Alam
- Version reviewed
- 1.0.0 · released 29 Oct 2026
- Stack
- Laravel 12 · PHP 8.3+ (CI runs 8.3 and 8.4) · MySQL 8 / MariaDB 10.6+ (SQLite for trials)
- Built with
- Claude Code
- Review period
- 28 Oct 2026 – 29 Oct 2026
- ✓AI code audit6 checks · 27 Oct 2026
- ✓Installed & run29 Oct 2026
- ✓Demo vs delivered29 Oct 2026
- ✓Final sign-off29 Oct 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !15 of 25 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 78/100 with no failing check.
- !2 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | All regex candidates are placeholders, validation rules, env references or runtime-generated passwords and test tokens. The only item worth noting is a literal 'CHANGE-ME' password in a RouterOS command snippet that buyers might paste verbatim. | 93 | Pass |
| Dependency vulnerabilities | The Laravel app ships composer.lock and the Android shell ships package-lock.json and yarn.lock, with Capacitor pinned exactly. I could only see composer.json and package.json, not the lockfile contents, so I could not check installed versions against advisories. The README claims 'composer audit' is clean, but this is unverified. | 82 | Pass |
| Authorisation & access control | The documented design is solid: permission middleware, visibleTo() scopes, route binding for IDOR protection, Sanctum token abilities, hashed passwords via Password:[hidden], and tests for IDOR. However a project file, a project file and most controllers were not in the digest, so no route could be traced end to end. A few visible items also need attention. | 72 | Warning |
| Database access rules | The digest never included a project file, the ISP migration, the models, Sql.php, RadiusDriver.php or the report queries. Project rules (query builder only, visibleTo scopes, route binding for IDOR protection) and the claimed security tests are good signs, but they cannot be confirmed from the code shown. The score is capped until the raw-SQL and schema areas are reviewed. | 70 | Warning |
| Code structure & duplication | The visible structure separates billing, network, payments, notifications and admin controllers into clear namespaces, and controllers delegate to services and Form Requests. The main maintainability costs are a shared CRUD base pattern that other controllers must follow and a few hard-coded values that belong in configuration; the digest does not show enough of the codebase to confirm the largest files. | 88 | Pass |
| Build reproducibility | Manifests are coherent: composer.json requires PHP ^8.3 with Laravel 12, a lockfile is present, and the mobile app pins exact Capacitor versions with lockfiles. No build output or vendor folders appear committed, and the setup flow (copy .env, key:generate, linkhive:install) is documented across several files. HowToSetup.md and the Docker files were not fully visible, so database creation and compose coherence could not be verified. | 86 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
The digest never included a project file, the ISP migration, the models, Sql.php, RadiusDriver.php or the report queries. Project rules (query builder only, visibleTo scopes, route binding for IDOR protection) and the claimed security tests are good signs, but they cannot be confirmed from the code shown. The score is capped until the raw-SQL and schema areas are reviewed.
The documented design is solid: permission middleware, visibleTo() scopes, route binding for IDOR protection, Sanctum token abilities, hashed passwords via Password:[hidden], and tests for IDOR. However a project file, a project file and most controllers were not in the digest, so no route could be traced end to end. A few visible items also need attention.
Requirement list
What the builder agreed to deliver before uploading — 15 of 25 met.
- Complete source of every part Partial
- No real credentials Met
- Single example environment file Partial
- Pinned dependencies Partial
- Database creates from empty Partial
- HowToSetup with two targets Partial
- Working demo Partial
- Authorisation on every write route Partial
- Five differentiators actually exist (nice)Partial
- Seed data (nice)Met
- AI tooling guide (nice)Met
- Changelog starting at 1.0.0 (nice)Met
- Container setup (nice)Partial
- Code structure for extension (nice)Partial
- README.md Met
- HowToSetup.md Met
- Laravel a project filee Met
- Laravel a project file Met
- a project file Met
- CLAUDE.md (nice)Met
- CHANGELOG.md (nice)Met
- LICENSE-NOTE.md (nice)Met
- a project file (nice)Met
- docker-compose.yml (nice)Met
- docs/ (optional)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 29 Oct 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 29 Oct 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 29 Oct 2026 with 2 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.