‹ GetRavista: Agency Project Management & Client Approval SaaSQuality report QR-26-00087
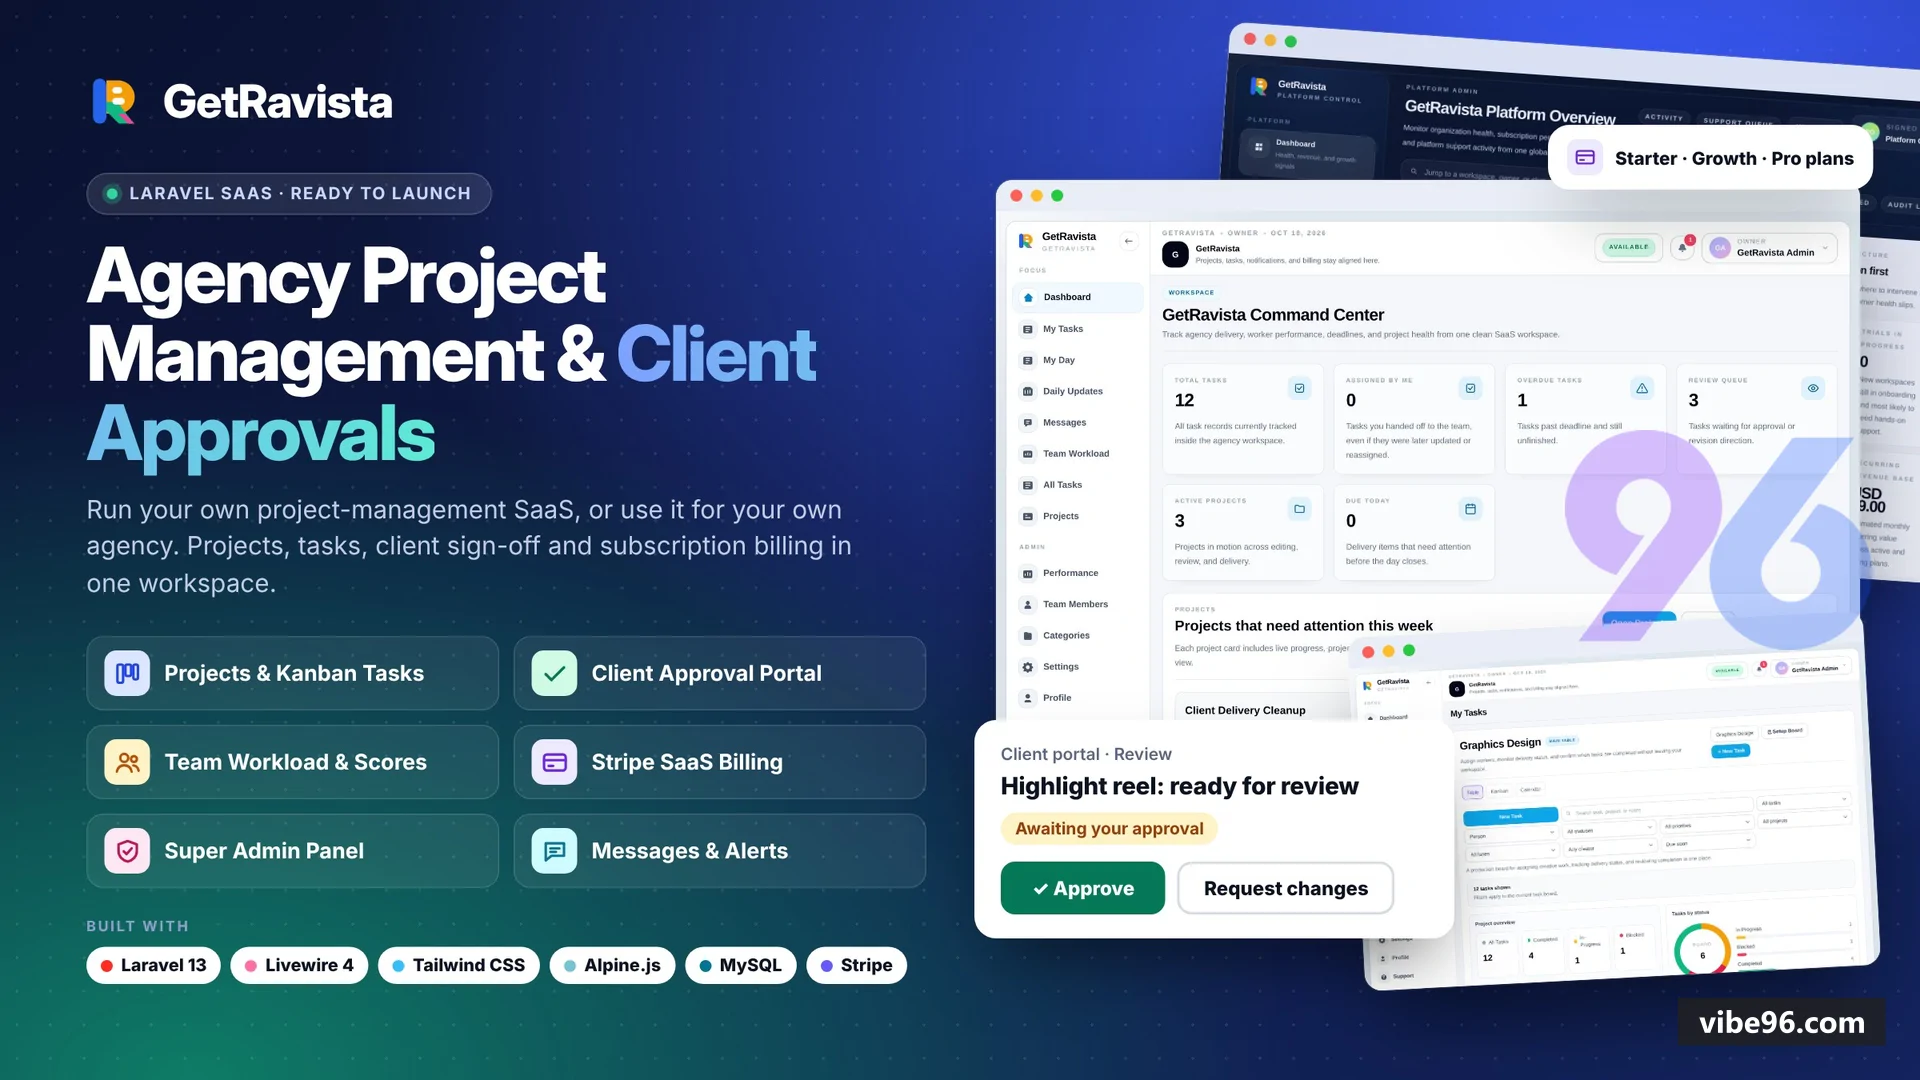
GetRavista: Agency Project Management & Client Approval SaaS
Agency project management SaaS with client approvals, task boards, messaging and Stripe billing
- Product ID
- B0148-56050
- Builder
- AHMAD
- Version reviewed
- 1.3.0 · released 4 Nov 2026
- Stack
- Laravel 13, Livewire 4 · PHP 8.4 · MySQL 8 / MariaDB 10.6
- Built with
- OpenAI Codex, Claude Code
- Review period
- 3 Nov 2026 – 4 Nov 2026
- ✓AI code audit6 checks · 3 Nov 2026
- ✓Installed & run3 Nov 2026
- ✓Demo vs delivered4 Nov 2026
- ✓Final sign-off4 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 7 of 7 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- ✓15 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 83/100 with no failing check.
- !3 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every regex candidate is a placeholder in docs (sk_test_..., sk-ant-..., whsec_..., your-random-secret-here) or a PHP reference such as Password:[hidden] or config() lookups. No committed .env, private keys or live tokens appeared in the digest. Not every file was visible, so the pass rests on the candidates shown. | 96 | Pass |
| Dependency vulnerabilities | Both composer.lock and package-lock.json are present, and composer.json and package.json use caret/tilde ranges on current major versions (Laravel 13, Livewire 4, Stripe 17, Vite 8). No wildcard or pre-release constraints are visible. The lockfile contents were omitted from the digest, so installed versions could not be checked against advisories. | 85 | Pass |
| Authorisation & access control | Visible routes sit behind auth, workspace, role and subscription middleware, and the exports check roles, project ownership and policies. The digest truncates web.php, the Livewire components and the services, so several mutating endpoints and id lookups could not be traced. Those gaps keep the score below the top band. | 80 | Warning |
| Database access rules | The files shown (RegisteredUserController, ExportController, routes) use Eloquent, validation and policy checks, and no string-built SQL or unscoped deletes appear. The services, Livewire components, models and migrations that carry the real query logic (TaskQueryService, QuickFind, Directory, GuestWorkspaceService) were not in the digest. The score is capped until those are reviewed. | 72 | Warning |
| Code structure & duplication | The project follows a clear domain split: Livewire components, one service per domain, policies and a BelongsToOrganization trait, with large Livewire components split into Concerns traits. Remaining issues are mostly small: a duplicated project-scoping lookup and some business logic in export and registration paths that could be moved into services. | 84 | Pass |
| Build reproducibility | composer.json pins PHP ^8.4, Laravel 13, Livewire 4 and the lockfiles are present. The setup script runs install, .env copy, key:generate and getravista:install in a sensible order. Gaps: compiled assets are committed in public/build, and the digest did not show the setup document's database creation step or the Node and database prerequisites. | 78 | Warning |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
composer.json pins PHP ^8.4, Laravel 13, Livewire 4 and the lockfiles are present. The setup script runs install, .env copy, key:generate and getravista:install in a sensible order. Gaps: compiled assets are committed in public/build, and the digest did not show the setup document's database creation step or the Node and database prerequisites.
Visible routes sit behind auth, workspace, role and subscription middleware, and the exports check roles, project ownership and policies. The digest truncates web.php, the Livewire components and the services, so several mutating endpoints and id lookups could not be traced. Those gaps keep the score below the top band.
The files shown (RegisteredUserController, ExportController, routes) use Eloquent, validation and policy checks, and no string-built SQL or unscoped deletes appear. The services, Livewire components, models and migrations that carry the real query logic (TaskQueryService, QuickFind, Directory, GuestWorkspaceService) were not in the digest. The score is capped until those are reviewed.
Requirement list
What the builder agreed to deliver before uploading — 15 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Met
- Pinned dependencies without critical CVEs (nice)Met
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 3 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | N/A | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 4 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 4 Nov 2026 with 3 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.3.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.