‹ StockMeta AI v8 — AI Metadata, SEO & Prompt Suite for CreatorsQuality report QR-26-00098
StockMeta AI v8 — AI Metadata, SEO & Prompt Suite for Creators
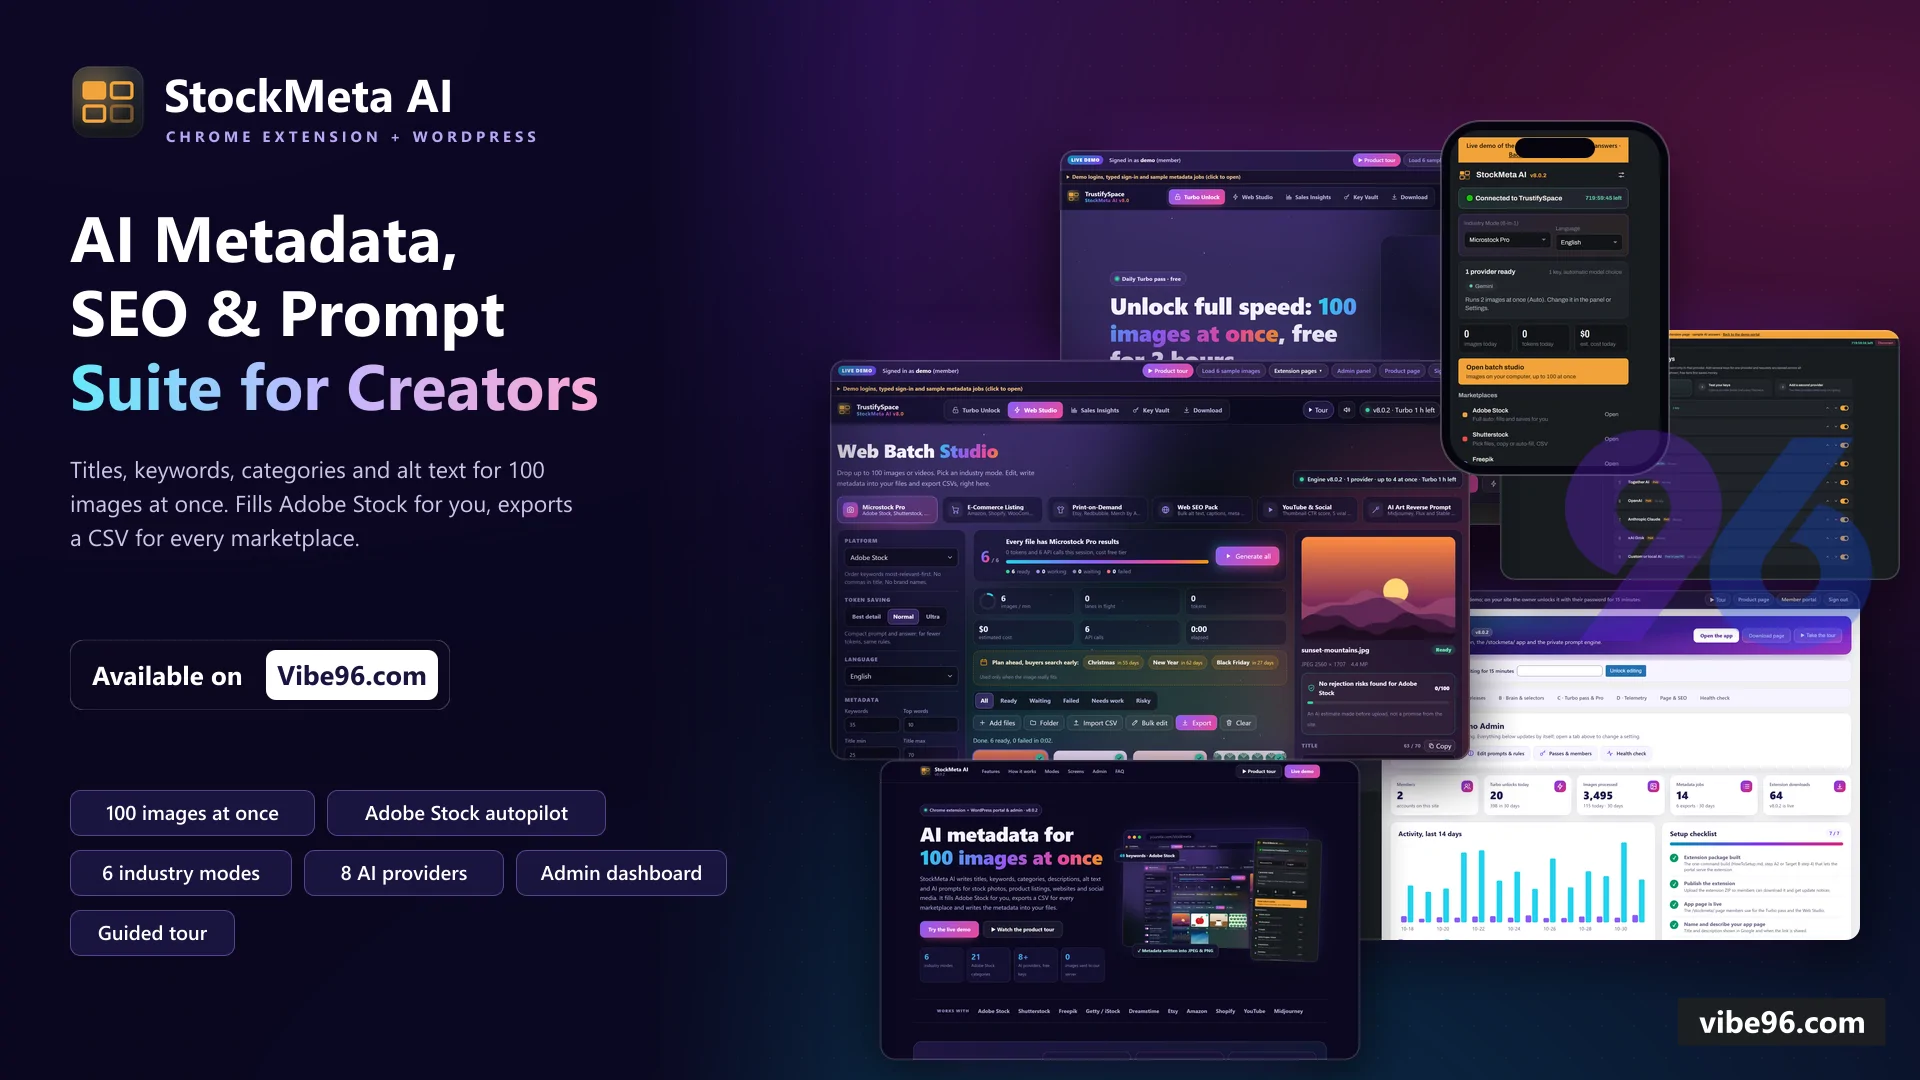
Chrome extension + WordPress portal: AI metadata for 100 images at once, your own key.
- Product ID
- B0577-60046
- Builder
- Abdullah Al Zabir
- Version reviewed
- 1.0.0 · released 5 Nov 2026
- Stack
- WordPress 6.8+ plugin with no PHP or JS framework dependencies (composer.json and package.json declare none) · PHP 8.3–8.5 (server plugin) and vanilla JavaScript (extension and portal UI, no framework) · MariaDB 10.11+ or MySQL 8.0+
- Built with
- Claude Code
- Review period
- 30 Oct 2026 – 5 Nov 2026 · 1 round of changes
- ✓AI code audit6 checks · 30 Oct 2026
- ✓Installed & run5 Nov 2026
- ✓Demo vs delivered5 Nov 2026
- ✓Final sign-off5 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 3 of 3 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !12 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 83/100 with no failing check.
- !3 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every secret-scan candidate is an environment-variable reference with fail-fast syntax, a JavaScript/PHP variable named 'token', or a test fixture. .env.example ships blank values and the docs state demo logins are never shipped in the archive. The only note is that the demo cookie value in the live probe is a runtime session ID, not a committed secret. | 96 | Pass |
| Dependency vulnerabilities | All manifests (root, extension, WordPress plugin) declare empty dependencies and devDependencies, so there is no third-party package surface to carry known CVEs. Lockfiles exist for npm and Composer, and Docker images are pinned to specific patch versions. Minor notes only: the base image pins will need periodic bumping, and the lockfile contents were not shown. | 92 | Pass |
| Authorisation & access control | The visible code shows layered guards: a token middleware with CSRF nonce, signed-token identity, and installation-ownership checks, plus a secure-origin check and login lockout on the auth routes. The route table, the admin controllers and the stats/jobs/exports handlers were not included in the excerpts, so admin role checks and per-id ownership checks could not be confirmed. A few design choices also deserve attention. | 72 | Warning |
| Database access rules | The digest shows a documented SQL inventory using $wpdb placeholders (%d, %s) with identifiers taken only from the prefix and fixed lists, and scoped deletes (user_id, day LIMIT). However, schema.sql, class-tsc-stockmeta-schema.php, jobs and the seed file were not included, so foreign keys, indexes and cascade rules are unverified. The score is capped until those files can be reviewed. | 80 | Warning |
| Code structure & duplication | Checked by our reviewers during the human review. | 70 | Warning |
| Build reproducibility | Manifests, lockfiles and docker-compose are coherent: PHP 8.3, Node 22, WordPress 6.8 and MariaDB 10.11 versions agree, and required env vars fail fast. HowToSetup.md was not included in the digest, and a few ordering and prerequisite points (build before compose, plugin cloud-bundle contents) depend on documentation we could not see. | 82 | Warning |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
Manifests, lockfiles and docker-compose are coherent: PHP 8.3, Node 22, WordPress 6.8 and MariaDB 10.11 versions agree, and required env vars fail fast. HowToSetup.md was not included in the digest, and a few ordering and prerequisite points (build before compose, plugin cloud-bundle contents) depend on documentation we could not see.
The digest shows a documented SQL inventory using $wpdb placeholders (%d, %s) with identifiers taken only from the prefix and fixed lists, and scoped deletes (user_id, day LIMIT). However, schema.sql, class-tsc-stockmeta-schema.php, jobs and the seed file were not included, so foreign keys, indexes and cascade rules are unverified. The score is capped until those files can be reviewed.
The visible code shows layered guards: a token middleware with CSRF nonce, signed-token identity, and installation-ownership checks, plus a secure-origin check and login lockout on the auth routes. The route table, the admin controllers and the stats/jobs/exports handlers were not included in the excerpts, so admin role checks and per-id ownership checks could not be confirmed. A few design choices also deserve attention.
Requirement list
What the builder agreed to deliver before uploading — 12 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Partial
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Partial
- Pinned dependencies without critical CVEs (nice)Met
- Documentation set (nice)Met
- Working live demo Partial
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 5 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | N/A | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | N/A | |
| Every module in the feature list opens and works | N/A | |
| No real secrets in the archive | N/A | |
| Branding and company details can be changed without code | N/A |
Stage 2 — Live demo compared with the delivered code
Completed 5 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 5 Nov 2026 with 3 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.