‹ Xmanager - All-in-one back office operations managerQuality report QR-26-00105
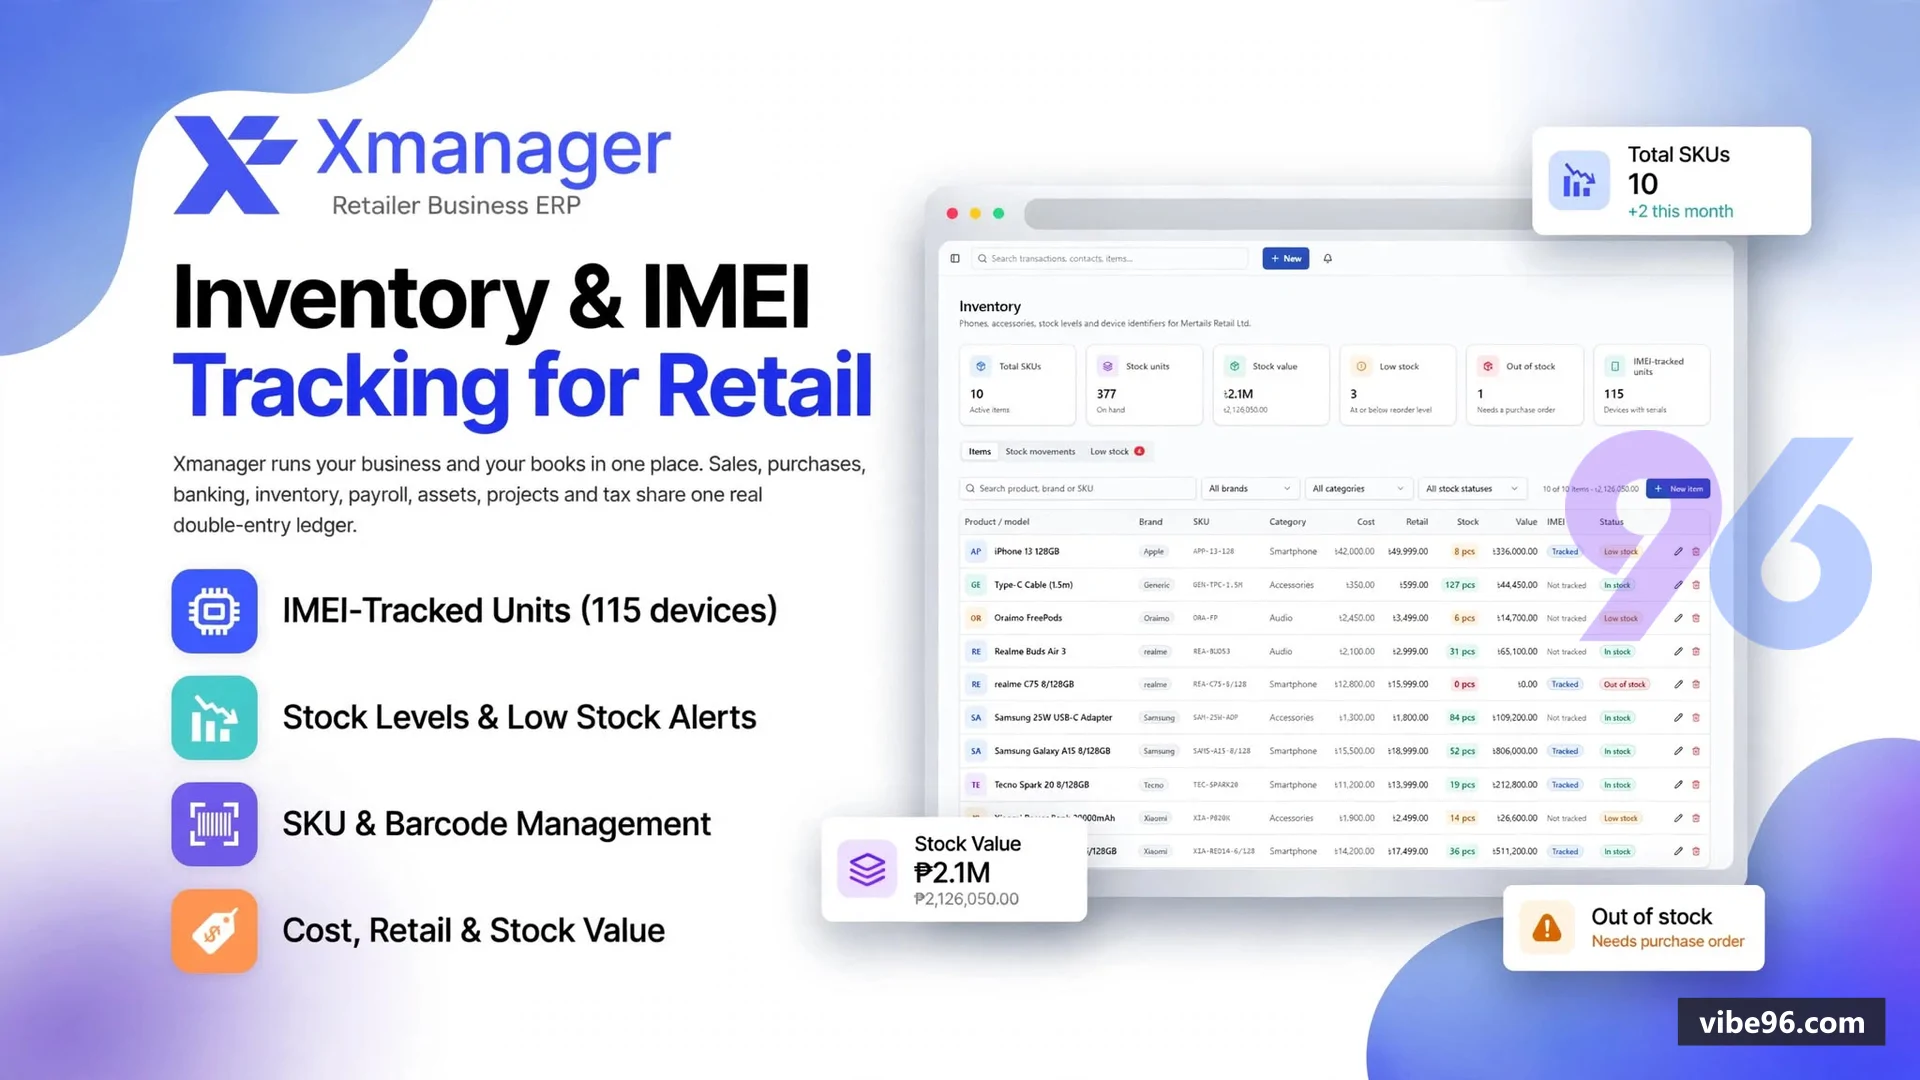
Xmanager - All-in-one back office operations manager
Multi-tenant double-entry accounting and operations platform for small business owners and bookkeepers
- Product ID
- B0656-97672
- Builder
- Md Jefranul Islam Rakib
- Version reviewed
- 1.0.0 · released 6 Nov 2026
- Stack
- TanStack Start 1.169 + React 19 · TypeScript 5.8 · PostgreSQL 14+ (Supabase)
- Built with
- Claude Code, Lovable
- Review period
- 25 Oct 2026 – 6 Nov 2026 · 2 rounds of changes
- ✓AI code audit6 checks · 23 Oct 2026
- ✓Installed & run6 Nov 2026
- ✓Demo vs delivered6 Nov 2026
- ✓Final sign-off6 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !13 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 77/100.
- !5 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | The database seed file contains a demo account password ([hidden]) which is acceptable for seeding but should be documented as needing change in production. All .env files are examples with placeholders. No real API keys, private keys, or production credentials were found. The Bearer token extraction code is standard auth middleware, not a hardcoded secret. | 95 | Warning |
| Dependency vulnerabilities | a project file has a lockfile (package-lock.json) with no known critical vulnerabilities in the declared dependencies. Several packages are outdated (e.g., @supabase/supabase-js 2.105.4 vs. latest 2.47+, jspdf 4.2.1 is very old). The database/ folder has schema.sql and seed.sql but no dependency manifest—acceptable for raw SQL. Bun.lock is present but not analyzed (Bun runtime). Overall safe for production with routine updates recommended. | 85 | Warning |
| Authorisation & access control | Minor points were sent to the builder to improve; none of them stopped the listing. | 45 | Fail |
| Database access rules | All queries use Supabase client with parameterized calls—no SQL injection risk. Row-level security policies enforce multi-tenant isolation. Schema is complete and can be created from empty. Findings: several foreign key columns lack indexes (e.g. journal_lines.account_id, invoices.customer_id), which will hurt performance under load. No unscoped deletes or updates found. | 92 | Warning |
| Code structure & duplication | Module boundaries are generally sound—business logic (accounting.ts, sales.ts, purchases.ts) is cleanly separated from routes and components, and Supabase integration is properly isolated. However, several UI components are large and contain repeated form/table patterns, and some hard-coded values (e.g., trial period, Stripe price ID) should be centralized. No dead code detected, but refactoring would improve maintainability. | 72 | Warning |
| Build reproducibility | The project can build (npm ci && npm run build works), but HowToSetup.md omits critical Supabase configuration steps: no instructions for creating the database, applying migrations, or seeding demo data. The setup document jumps directly to 'set env vars' without explaining how to obtain them or initialize the schema. Docker setup references supabase/migrations/ but doesn't document the migration application order or how to run seed.sql. | 72 | Warning |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
All queries use Supabase client with parameterized calls—no SQL injection risk. Row-level security policies enforce multi-tenant isolation. Schema is complete and can be created from empty. Findings: several foreign key columns lack indexes (e.g. journal_lines.account_id, invoices.customer_id), which will hurt performance under load. No unscoped deletes or updates found.
The database seed file contains a demo account password ([hidden]) which is acceptable for seeding but should be documented as needing change in production. All .env files are examples with placeholders. No real API keys, private keys, or production credentials were found. The Bearer token extraction code is standard auth middleware, not a hardcoded secret.
a project file has a lockfile (package-lock.json) with no known critical vulnerabilities in the declared dependencies. Several packages are outdated (e.g., @supabase/supabase-js 2.105.4 vs. latest 2.47+, jspdf 4.2.1 is very old). The database/ folder has schema.sql and seed.sql but no dependency manifest—acceptable for raw SQL. Bun.lock is present but not analyzed (Bun runtime). Overall safe for production with routine updates recommended.
Module boundaries are generally sound—business logic (accounting.ts, sales.ts, purchases.ts) is cleanly separated from routes and components, and Supabase integration is properly isolated. However, several UI components are large and contain repeated form/table patterns, and some hard-coded values (e.g., trial period, Stripe price ID) should be centralized. No dead code detected, but refactoring would improve maintainability.
The project can build (npm ci && npm run build works), but HowToSetup.md omits critical Supabase configuration steps: no instructions for creating the database, applying migrations, or seeding demo data. The setup document jumps directly to 'set env vars' without explaining how to obtain them or initialize the schema. Docker setup references supabase/migrations/ but doesn't document the migration application order or how to run seed.sql.
Requirement list
What the builder agreed to deliver before uploading — 13 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Partial
- Pinned dependencies without critical CVEs (nice)Partial
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 6 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 6 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 6 Nov 2026 with 5 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.