‹ Axioz ERPQuality report QR-26-00126
Axioz ERP
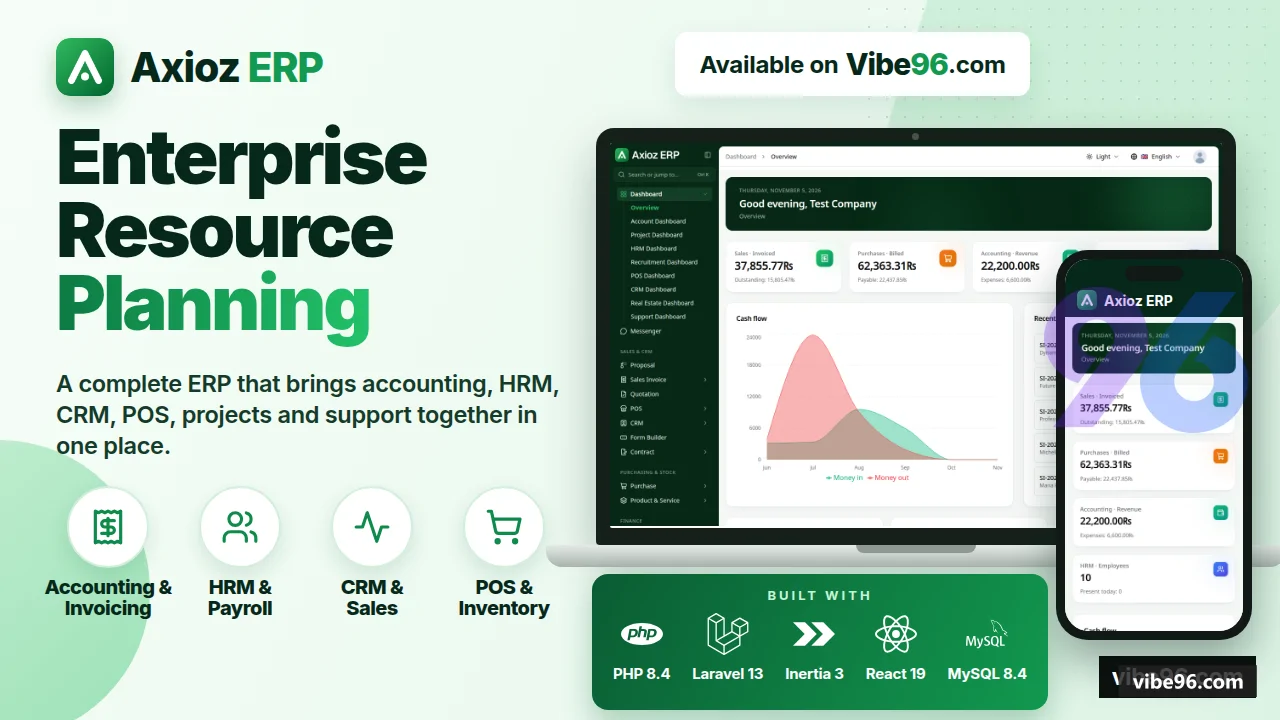
Multi-tenant Laravel and React ERP/SaaS platform: super admin sells plans to companies running 32 business modules.
- Product ID
- B0842-86888
- Builder
- Md Sajjad Hossain
- Version reviewed
- 1.0.0 · released 12 Nov 2026
- Stack
- Laravel 13.40 with Inertia 3 and React 19 · PHP 8.4+ (TypeScript 5.9 frontend) · MySQL 8.0+
- Built with
- Claude Code
- Review period
- 10 Nov 2026 – 12 Nov 2026
- ✓AI code audit6 checks · 9 Nov 2026
- ✓Installed & run12 Nov 2026
- ✓Demo vs delivered12 Nov 2026
- ✓Final sign-off12 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !21 of 25 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 81/100 with no failing check.
- !3 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every regex candidate is a placeholder, a generated-at-install value, a code reference to a stored setting, or a test fixture. .env.example keeps APP_KEY and all secrets empty, and the Makefile generates random DB passwords with openssl. The 4.5 MB seed.sql and the demo login values were not visible in the digest and should be checked before release. | 92 | Pass |
| Dependency vulnerabilities | composer.json and package.json use caret ranges with no wildcards or 'latest'. README and a project file claim composer.lock (171 packages) and package-lock.json (639) exist with zero known vulnerabilities, but lockfiles were omitted from the digest, so the installed versions could not be checked. A few dev-tooling and bleeding-edge major choices deserve a note. | 82 | Pass |
| Authorisation & access control | The visible code and docs describe a well-structured authorization model: permission checks in controllers and form requests, plan checks via middleware, tenant scoping via a global trait, and Hash::make for passwords. However, the route files (web.php, api.php, module routes) and nearly all controllers were not provided, so I could not trace individual endpoints. Score reflects the evidence of a mature approach, discounted for unverified coverage. | 78 | Warning |
| Database access rules | The project documents a tenant-scoped ORM layer (TenantScoped trait), a schema.sql with primary keys, 714 foreign keys and indexed tenant columns, and a raw-query audit. The digest, however, does not include any controller, model or migration source that touches the database, so these claims could not be checked. The score is capped until the queries can be reviewed. | 72 | Warning |
| Code structure & duplication | The project separates core code from 32 modules under Modules/, with per-module routes, pages and permission seeders, which is easy to follow. The digest does not show file sizes for the largest controllers, so oversized-file and duplication claims cannot be fully verified, and the 181 extractor classes in the Webhook module suggest repeated patterns worth consolidating. | 84 | Warning |
| Build reproducibility | The project ships composer.json, package.json, lockfiles (per README), .env.example, schema.sql, a Makefile and HowToSetup.md, and excludes vendor, node_modules and public/build. The digest was truncated, so HowToSetup.md step order, docker-compose coherence and the a project file referenced by `make package` could not be verified. A few small inconsistencies are noted below. | 80 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
The project separates core code from 32 modules under Modules/, with per-module routes, pages and permission seeders, which is easy to follow. The digest does not show file sizes for the largest controllers, so oversized-file and duplication claims cannot be fully verified, and the 181 extractor classes in the Webhook module suggest repeated patterns worth consolidating.
The visible code and docs describe a well-structured authorization model: permission checks in controllers and form requests, plan checks via middleware, tenant scoping via a global trait, and Hash::make for passwords. However, the route files (web.php, api.php, module routes) and nearly all controllers were not provided, so I could not trace individual endpoints. Score reflects the evidence of a mature approach, discounted for unverified coverage.
The project documents a tenant-scoped ORM layer (TenantScoped trait), a schema.sql with primary keys, 714 foreign keys and indexed tenant columns, and a raw-query audit. The digest, however, does not include any controller, model or migration source that touches the database, so these claims could not be checked. The score is capped until the queries can be reviewed.
Requirement list
What the builder agreed to deliver before uploading — 21 of 25 met.
- Complete source for every part Met
- No real credentials Met
- Lockfiles and pinned dependencies Partial
- Schema creates from empty Met
- Tenant isolation and role checks Partial
- Parameterised queries and scoped deletes Met
- HowToSetup.md with at least two targets Met
- Reachable demo with working credentials Partial
- README.md and licence note Partial
- CLAUDE.md or AGENTS.md (nice)Met
- CHANGELOG.md starting at 1.0.0 (nice)Met
- Seed data (nice)Met
- Docker and docs (optional)Met
- README.md Met
- HowToSetup.md Met
- Laravel a project filee Met
- Laravel a project file Met
- Laravel a project file Met
- a project file Met
- CLAUDE.md (nice)Met
- CHANGELOG.md (nice)Met
- a project file (nice)Met
- docker-compose.yml (nice)Met
- a project file (optional)Met
- LICENSE-NOTE.md (optional)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 12 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 12 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 12 Nov 2026 with 3 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.