‹ NexaTechQuality report QR-26-00004
NexaTech
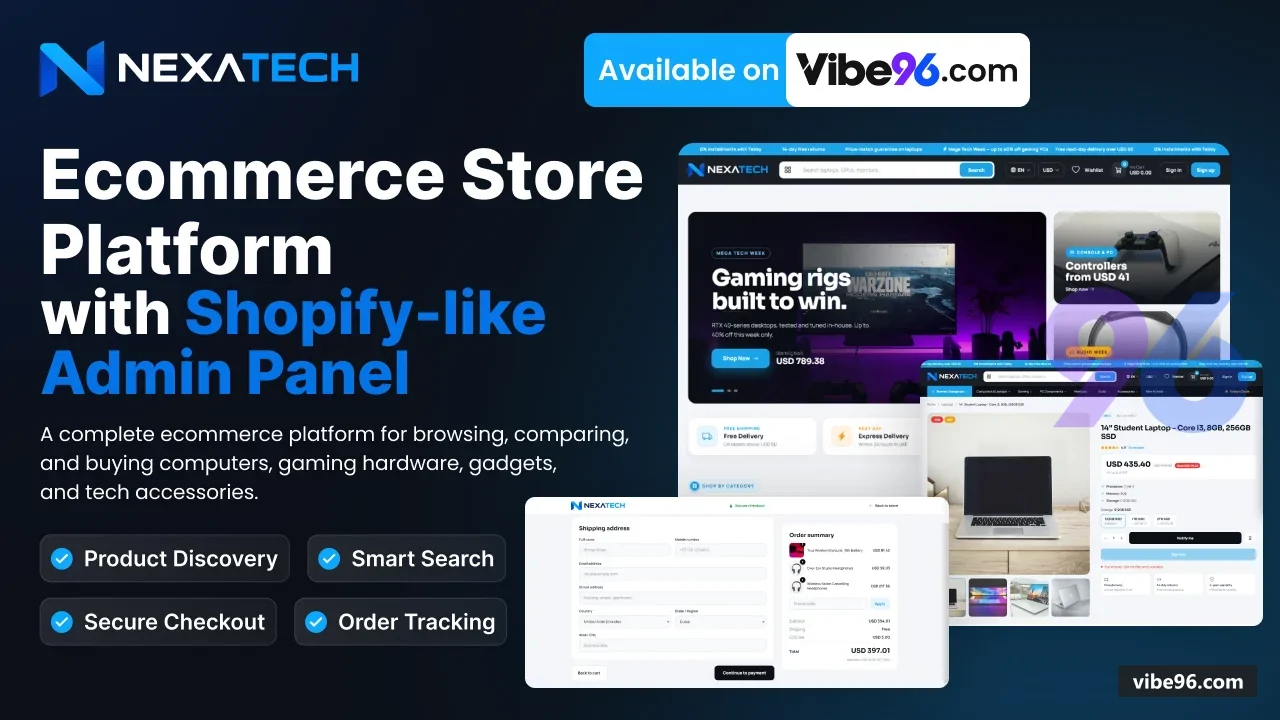
A ready-to-launch Laravel electronics store with an English/Arabic storefront and a full admin panel, for retailers.
- Product ID
- B0001-74510
- Builder
- X1980 Group
- Version reviewed
- 1.0.0 · released 4 Oct 2026
- Stack
- Laravel · PHP 8.x · MySQL 8.0 / MariaDB 10.6
- Built with
- Claude Code
- Review period
- 4 Oct 2026 – 4 Oct 2026
- ✓AI code audit6 checks · 4 Oct 2026
- ✓Installed & run4 Oct 2026
- ✓Demo vs delivered4 Oct 2026
- ✓Final sign-off4 Oct 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- ✓15 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 92/100 with no failing check.
- !4 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | No real API keys or secrets found. The codebase uses environment variables correctly for all credentials. However, the demo mode configuration and example files contain weak placeholder patterns that could mislead buyers into using insecure defaults. The ADMIN_PASSWORD seeding logic allows empty values which generates strong passwords, but the demo setup uses a configurable password that buyers might set weakly. | 92 | Warning |
| Dependency vulnerabilities | Both composer.lock and package-lock.json are present with all dependencies pinned to exact versions. No known critical vulnerabilities detected in the declared versions. A few packages are slightly outdated (Laravel 12.69.2 vs current 12.x, Tailwind CSS 4.3.3 vs 4.x latest) but these are minor version differences with no security advisories. | 95 | Pass |
| Authorisation & access control | All admin routes require authentication via auth:admin middleware and role-based authorization through AuthorizeAdminArea. Storefront mutations (checkout, cart, orders) are properly guarded. However, customer account endpoints lack ownership checks (any signed-in user can read another's orders/addresses by ID), and the demo-reset endpoint is unguarded in non-demo mode. Passwords use bcrypt correctly. | 92 | Warning |
| Database access rules | No SQL injection paths found. Query builders and Eloquent are used correctly throughout. One unscoped delete in ProductTransferController (line 81) operates on a temporary token table and is acceptable. Schema migrations are complete with foreign keys and cascades. Minor gaps: several foreign key columns lack indexes (brand_id, category_id on products; user_id on wishlists/reviews), which will slow joins and lookups as data grows. | 92 | Warning |
| Code structure & duplication | The codebase follows Laravel conventions well with clear separation of concerns (Controllers, Services, Actions, Models). However, several files exceed 300 lines, some payment/shipping logic is duplicated across gateway implementations, and a few hard-coded values should move to configuration. The structure is maintainable but could be optimized. | 78 | Warning |
| Build reproducibility | The project is fully reproducible from source with locked dependencies (composer.lock, package-lock.json). HowToSetup.md covers both traditional and Docker deployment clearly. Minor issues: Docker compose references DB_ROOT_PASSWORD without documenting it in .env.example comments; the setup doc could be clearer about when to run migrations vs. seed; npm scripts reference 'concurrently' which is a dev dependency (correct but could confuse). | 92 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
No real API keys or secrets found. The codebase uses environment variables correctly for all credentials. However, the demo mode configuration and example files contain weak placeholder patterns that could mislead buyers into using insecure defaults. The ADMIN_PASSWORD seeding logic allows empty values which generates strong passwords, but the demo setup uses a configurable password that buyers might set weakly.
All admin routes require authentication via auth:admin middleware and role-based authorization through AuthorizeAdminArea. Storefront mutations (checkout, cart, orders) are properly guarded. However, customer account endpoints lack ownership checks (any signed-in user can read another's orders/addresses by ID), and the demo-reset endpoint is unguarded in non-demo mode. Passwords use bcrypt correctly.
No SQL injection paths found. Query builders and Eloquent are used correctly throughout. One unscoped delete in ProductTransferController (line 81) operates on a temporary token table and is acceptable. Schema migrations are complete with foreign keys and cascades. Minor gaps: several foreign key columns lack indexes (brand_id, category_id on products; user_id on wishlists/reviews), which will slow joins and lookups as data grows.
The codebase follows Laravel conventions well with clear separation of concerns (Controllers, Services, Actions, Models). However, several files exceed 300 lines, some payment/shipping logic is duplicated across gateway implementations, and a few hard-coded values should move to configuration. The structure is maintainable but could be optimized.
Requirement list
What the builder agreed to deliver before uploading — 15 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Met
- Pinned dependencies without critical CVEs (nice)Met
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 4 Oct 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 4 Oct 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 4 Oct 2026 with 4 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.