
‹ Look FashionQuality report QR-26-00114
Look Fashion
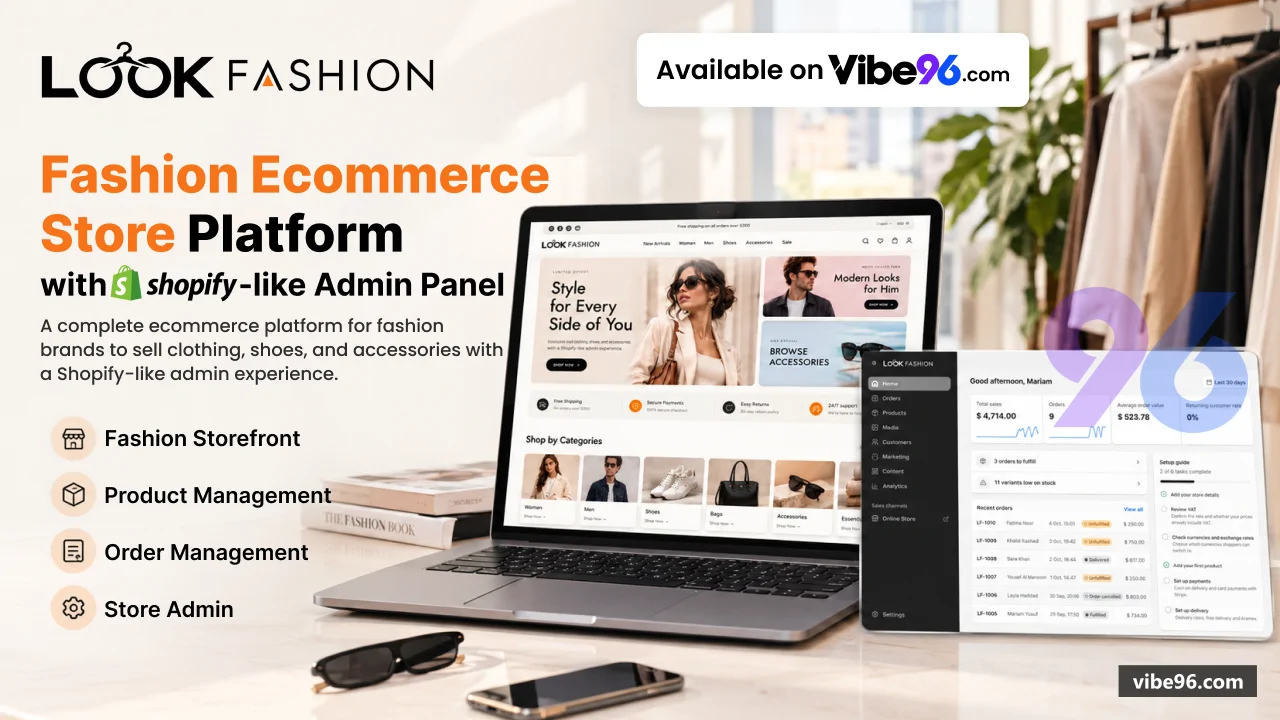
Complete fashion e-commerce platform with bilingual storefront and Shopify-style admin for clothing retailers
- Product ID
- B0002-47813
- Builder
- Buildify
- Version reviewed
- 1.9.0 · released 11 Nov 2026
- Stack
- Laravel 12.69 · PHP 8.2+ · MySQL 8 / MariaDB 10.11
- Built with
- Claude Code
- Review period
- 10 Nov 2026 – 11 Nov 2026
- ✓AI code audit6 checks · 10 Nov 2026
- ✓Installed & run11 Nov 2026
- ✓Demo vs delivered11 Nov 2026
- ✓Final sign-off11 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !12 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 84/100 with no failing check.
- !4 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every regex candidate in the digest is a variable assignment, a validation pattern, a Laravel Password/token call or a test fixture, not a real credential. The .env.example uses empty placeholders and no committed .env is visible. The digest was truncated, so the unseen files (about 217 changed files, config and deploy files) are not fully verified. | 90 | Pass |
| Dependency vulnerabilities | composer.json and composer.lock exist (the lock is 306 KB) and were changed since the last audit. Their contents were not in the digest, so I could not verify installed versions, advisories or version ranges. No package.json or package-lock.json is listed even though the project mentions a Vite front-end build, and DEPENDENCIES.md and the CI workflow were deleted. | 70 | Warning |
| Authorisation & access control | Of the files shown, the address book scopes every lookup to the signed-in customer, the CSV import uses UUID tokens on a private disk, and the payment webhook verifies with the provider before marking paid. Routes, admin middleware, the Policies and ReturnController/TrackOrderController/PaymentReturnController were not provided, so admin role checks and several id lookups could not be verified. | 80 | Warning |
| Database access rules | The visible controllers use Eloquent with bound parameters and correct ownership scoping (addresses scoped by user_id, orders reached by a 48-character token). The migrations and the changed DB-touching files (Cleanup, Search, CartService, DemoDataRun, DemoHistory) were not in the digest, so the schema checks for foreign keys, indexes and cascades and the raw-SQL checks could not be done. The score is held below 90 for that reason and for a few minor query issues. | 82 | Warning |
| Code structure & duplication | The project is organised into focused Actions, Services, Requests and Controllers, and CLAUDE.md documents a 300-line class limit enforced by a CodeRulesTest. The visible excerpts show no god files or copy-pasted modules, so the structure check is strong. | 88 | Pass |
| Build reproducibility | The digest shows a standard Laravel 12 layout with composer.json, composer.lock, .nvmrc, .env.example and HowToSetup.md. However, the contents of composer.json, package.json, HowToSetup.md and the nginx/docker configs were not provided, so reproducibility from a clean machine could not be confirmed. Several files changed since the last audit (CI workflow and DEPENDENCIES.md deleted), which reduces visible build documentation. | 72 | Warning |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
composer.json and composer.lock exist (the lock is 306 KB) and were changed since the last audit. Their contents were not in the digest, so I could not verify installed versions, advisories or version ranges. No package.json or package-lock.json is listed even though the project mentions a Vite front-end build, and DEPENDENCIES.md and the CI workflow were deleted.
The visible controllers use Eloquent with bound parameters and correct ownership scoping (addresses scoped by user_id, orders reached by a 48-character token). The migrations and the changed DB-touching files (Cleanup, Search, CartService, DemoDataRun, DemoHistory) were not in the digest, so the schema checks for foreign keys, indexes and cascades and the raw-SQL checks could not be done. The score is held below 90 for that reason and for a few minor query issues.
Of the files shown, the address book scopes every lookup to the signed-in customer, the CSV import uses UUID tokens on a private disk, and the payment webhook verifies with the provider before marking paid. Routes, admin middleware, the Policies and ReturnController/TrackOrderController/PaymentReturnController were not provided, so admin role checks and several id lookups could not be verified.
The digest shows a standard Laravel 12 layout with composer.json, composer.lock, .nvmrc, .env.example and HowToSetup.md. However, the contents of composer.json, package.json, HowToSetup.md and the nginx/docker configs were not provided, so reproducibility from a clean machine could not be confirmed. Several files changed since the last audit (CI workflow and DEPENDENCIES.md deleted), which reduces visible build documentation.
Requirement list
What the builder agreed to deliver before uploading — 12 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Partial
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Partial
- Pinned dependencies without critical CVEs (nice)Met
- Documentation set (nice)Met
- Working live demo Partial
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 11 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 11 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 11 Nov 2026 with 4 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.9.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Report history
| Report | Version | Date | Score | Status |
|---|---|---|---|---|
| QR-26-00114 | 1.9.0 | 11 Nov 2026 | 81 | Current |
| QR-26-00029 | 1.0.0 | 7 Oct 2026 | 84 | Replaced |
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.