‹ FrontDesk AIQuality report QR-26-00134
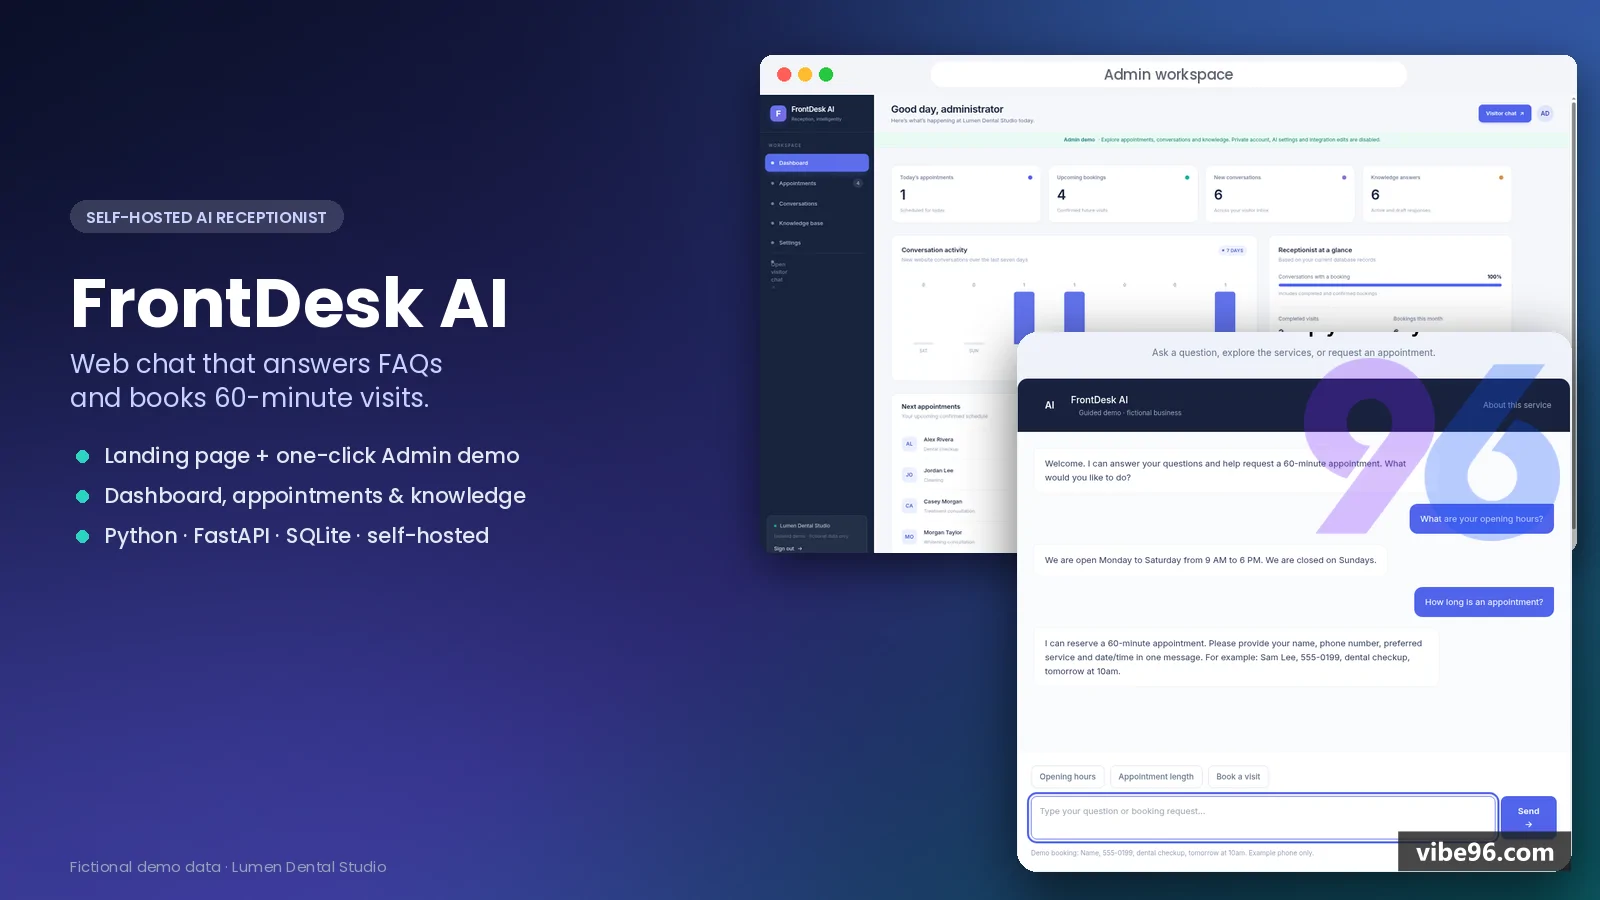
FrontDesk AI
Self-hosted AI receptionist that answers FAQs and books appointments via web chat for clinics, salons and service firms.
- Product ID
- B0639-75122
- Builder
- Syed Abue Tayeb Al-Zeyed
- Version reviewed
- 1.0.0 · released 13 Nov 2026
- Stack
- FastAPI 0.162 with Uvicorn 0.54 · Python 3.12 (python:3.12.7-slim image) · SQLite file via SQLAlchemy 2.0.57 (SQLite version not pinned)
- Built with
- Claude Code
- Review period
- 7 Nov 2026 – 13 Nov 2026
- ✓AI code audit6 checks · 7 Nov 2026
- ✓Installed & run13 Nov 2026
- ✓Demo vs delivered13 Nov 2026
- ✓Final sign-off13 Nov 2026
At a glance
- ✓Installed and run from the delivered code — 7 of 7 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !14 of 24 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 87/100 with no failing check.
- !1 open warning — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | Every regex candidate is either an empty env interpolation, a placeholder, a runtime-generated session/CSRF token, or a test variable. Both .env.example files have blank values, and the app refuses to start without a SECRET_KEY. The only note is that the digest was truncated, so the remaining files were not inspected. | 96 | Pass |
| Dependency vulnerabilities | The project ships FrontDesk a project file with exact pins, plus a requirements.lock that the Dockerfile installs with --require-hashes. The lockfile's contents were not in the digest, so I could not verify it. Several pinned versions (fastapi 0.162.0, uvicorn 0.54.0, cryptography 50.0.2, pydantic 2.14.3) are beyond what I can confirm and should be checked against the index. I know of no critical vulnerability in the packages I can identify. | 82 | Pass |
| Authorisation & access control | All admin routers sit behind a router-level require_admin dependency, and mutating handlers also verify CSRF. Passwords use bcrypt, setup needs a token, and public chat conversation IDs are bound to a session token. A few low-risk gaps remain, such as unchecked ownership on some demo-mode reads and files not visible in the digest. | 88 | Pass |
| Database access rules | The visible routes use SQLAlchemy ORM with parameterised queries, escaped LIKE terms and primary-key-scoped deletes, with no string-built SQL or injection path seen. However, a project file, models.py, database.py and web.py were not included in the digest, so foreign keys, indexes, cascades and the creation-from-empty requirement could not be confirmed. A few unbounded queries and a settings-table design add minor concerns. | 78 | Warning |
| Code structure & duplication | The app is organized into sensible feature modules (routes/admin split by dashboard, knowledge, settings, appointments, conversations; app/ split by security, auth, crypto, demo). Routers are small and readable. The main drawbacks are repeated guard boilerplate and some dense one-line handlers and duplicated pagination/demo checks. | 84 | Pass |
| Build reproducibility | The root Dockerfile, hashed requirements.lock, render.yaml and compose file form a coherent, documented path, and the live demo confirms the image builds and starts. Remaining gaps are minor: the declared stack is empty, runtime versions are not verifiably aligned, and the Go-based test helper needs an offline toolchain. | 82 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
The visible routes use SQLAlchemy ORM with parameterised queries, escaped LIKE terms and primary-key-scoped deletes, with no string-built SQL or injection path seen. However, a project file, models.py, database.py and web.py were not included in the digest, so foreign keys, indexes, cascades and the creation-from-empty requirement could not be confirmed. A few unbounded queries and a settings-table design add minor concerns.
Requirement list
What the builder agreed to deliver before uploading — 14 of 24 met.
- Complete source of every part Partial
- No real credentials Met
- Single example config file Partial
- SQLite schema creates from empty Partial
- Pinned dependencies with lockfile Partial
- Authorisation on every write route Partial
- HowToSetup.md with two targets Partial
- Working demo Partial
- README and licence note Partial
- CLAUDE.md for AI coding tools (nice)Met
- CHANGELOG starting at 1.0.0 (nice)Met
- Seed data (nice)Partial
- Docker support (nice)Met
- README.md Met
- HowToSetup.md Met
- .env.example Met
- requirements.txt Met
- requirements.lock Met
- a project file Met
- a project file (nice)Met
- CLAUDE.md (nice)Met
- CHANGELOG.md (nice)Met
- docker-compose.yml (nice)Met
- a project file (optional)Missing
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 13 Nov 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | N/A |
Stage 2 — Live demo compared with the delivered code
Completed 13 Nov 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 13 Nov 2026 with 1 warning shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.